Blink Wallet News: Few Dozen Custodial Accounts Hit, Services Resumed
Custodial Accounts Targeted, Services Paused
Blink Wallet News began on September 19, 2026. The Bitcoin service paused operations and said it was investigating a security incident.
An attacker reached a limited number of custodial accounts and withdrew funds. This crypto breach touched only users whose keys the platform holds. The company also said non-custodial wallets were unaffected.
How the Incident Unfolded Over Two Days
The Blink Wallet News timeline below comes from the official X profile, @blinkbtc. Times appear as shown on each post.
September 19, 6:11 PM IST: Services were paused. The company said the large majority of funds were secure.
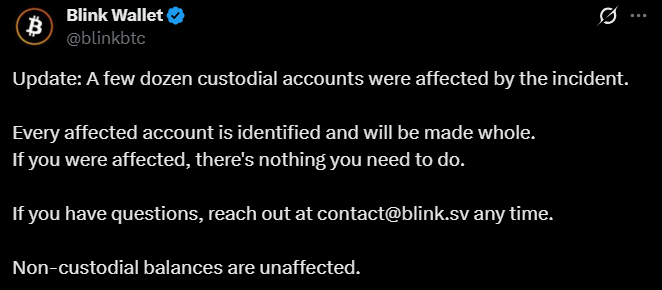
September 19, 9:36 PM IST: A few dozen custodial accounts were confirmed impacted.
September 20, 1:49 AM IST: Services returned online after the vulnerability was fixed and verified.
Roughly seven and a half hours passed between the first post and the restoration notice. Early hack reports gave few figures, and the second update narrowed the scope.
Source: Official X Post
Scale of the Losses and User Impact
This part of Blink Wallet News rests on the company's own statements. Confirmed points are below.
Scope: a few dozen custodial accounts were impacted.
Identification: every account involved has been identified.
Compensation: the company said impacted users will be made whole.
User action: impacted users need to do nothing.
Status: the accounts stay locked temporarily.
Missing details matter too. The company has not shared the total amount withdrawn or named the vulnerability. It promised a full post-mortem, meaning a detailed review written after an incident.
This report was written on September 20, 2026, and reflects only official posts published up to then.
Who Holds the Keys: Two Models Compared
The team stressed that non-custodial balances were never touched. The table below shows why the two models differ.
Feature | Custodial | Non-custodial |
Who holds the keys? | The service provider | The user |
Impact in this case | Some accounts hit. | Unaffected |
Official statement | Locked temporarily for impacted users | Balances were never affected. |
In a custodial setup, the provider controls access, so a provider-side flaw can expose user balances. Users who hold their own keys stayed out of this case. For Blink Wallet News readers, the split is the key point.
Fix Verified and Access Restored
On September 20, 2026, the team said services were back online. It added that the vulnerability was fixed and verified.
Access returned for all unaffected accounts. They can continue as usual. Impacted users remain locked out for now.
The team did not say how long the temporary lock will last. It also gave no date for the review.
Anyone with questions can use the support email in the official post. Readers can also check the official X profile and the project website for updates.
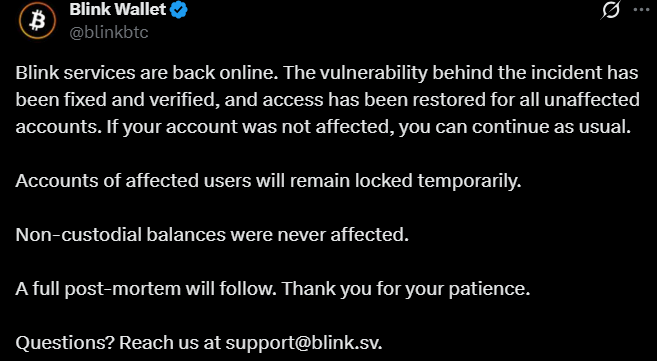
Source: X Post
Expert Opinion: Speed and Openness Under Pressure
A neutral read of the three posts shows several positives. The platform paused services quickly. It stated the scope within hours. It verified the fix before reopening access.
Open questions remain. The withdrawn amount, the root cause, and the timing of the full review are unconfirmed. This report avoids guessing on any of them.
Blink Wallet News also points to a wider lesson about custody. Keeping keys with a provider adds convenience but brings counterparty risk, meaning reliance on the provider's security. Self-custody removes that link but places full responsibility on the user.
Conclusion: What to Watch Next
The incident hit a few dozen customers whose keys the provider holds, while self-held balances stayed safe. Services are back, and the team reports the vulnerability as fixed and verified.
Watch for these next items:
The full post-mortem and its findings
The total amount withdrawn
When the temporary lock ends
YMYL Disclaimer: This article is for educational and informational purposes only. It is not financial advice, a price prediction, or a return guarantee. Readers should do their own research.