Bitget Hack Update: Withdrawals Restart as Exchange Recovers From Hack
Bitget Hack Update: $387M Theft, THORChain Dispute and Withdrawal Date
This Bitget hack update brings new answers. On September 28, Bitget CEO Gracy Chen explained how attackers took roughly $380M to $387.5M from the exchange. Part of the stolen money then moved through THORChain, which sparked a public dispute over decentralization. Here is what is confirmed so far, and what could come next.
At a Glance
-
Incident date: September 24, 2026
-
Estimated loss: About $380M to $387.5M
-
Cause: A third-party security product flaw and stolen internal access credentials
-
Private keys: They were not leaked
-
Cold wallets: Unaffected
-
THORChain: Used to swap part of the stolen assets
-
BTC withdrawals: Resumed September 28 at 08:00 UTC
-
Protection fund: To be restored to the $300M baseline
Bitget Security Incident: How Did the $380M Theft Happen?
The incident did not start with a leaked private key. Chen said hackers exploited a vulnerability in a third-party security product and stole internal network access credentials. They then forged withdrawal commands sent to the wallet system and bypassed risk checks to trigger abnormal transfers.
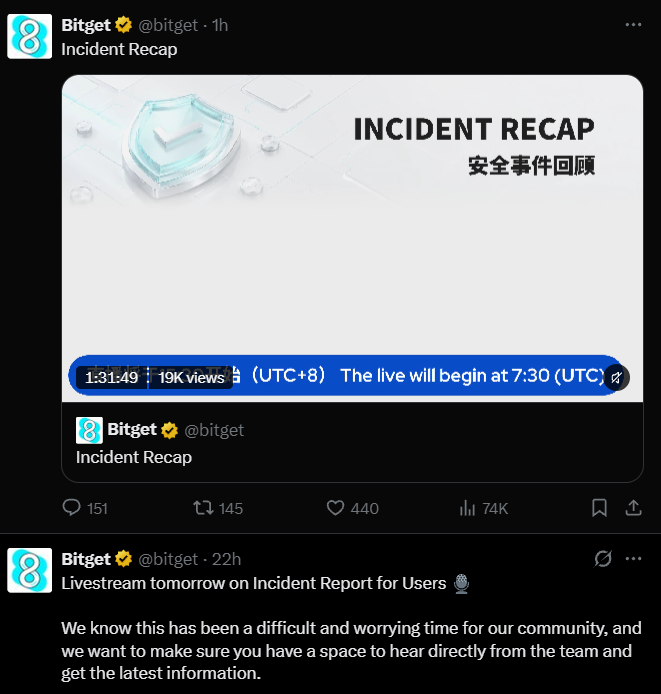
Source: Official Recap Post
That explains how so much value left without touching the cold wallet. A full technical breakdown will come in a later security report.
| Key Detail | What Exchange Said |
| Attack date | September 24, 2026 |
| Entry point | Third-party security product vulnerability |
| Compromised access | Internal network credentials |
| Attacker action | Forged withdrawal commands |
| Risk controls | Bypassed |
| Private keys | Not leaked |
| Cold wallets | Unaffected |
Where Did the Stolen Bitget Funds Go?
Some of the stolen Bitget Exchange funds were swapped across chains. Security firm GoPlus reported that about 101.5 BTC (roughly $8.5M) had left through THORChain, with around 27.63M XRP (about $43M) still mid-swap into BTC at the time. These are early estimates from third parties, not final loss or recovery totals.
Cross-chain protocols matter because they let attackers change assets quickly, which makes tracing harder. Exchanges and blockchain security firms continue to monitor the publicly listed attacker addresses.
THORChain Bitget Hack Response
Gracy Chen formally asked THORChain to refuse service to the confirmed attacker addresses. She argued that decentralization is a design principle and not a shield for moving known stolen funds.
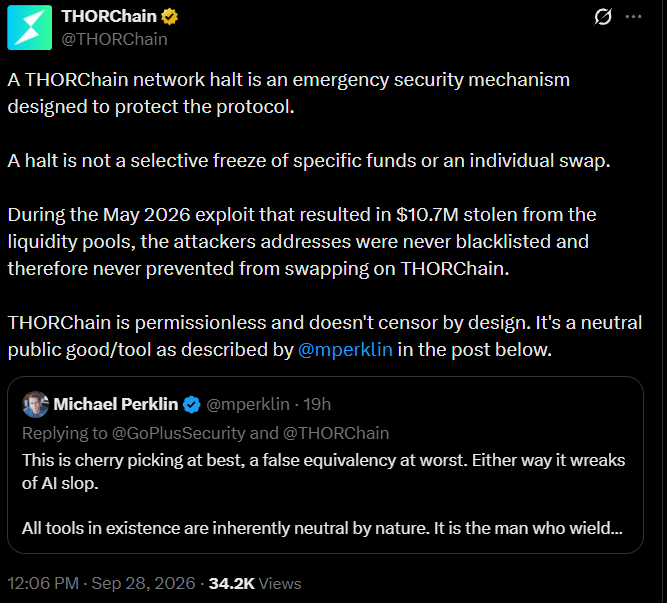
THORChain replied that a network halt is an emergency security tool and not a selective freeze on specific addresses or single swaps. It also said attacker addresses were never blacklisted after its own $10.7M exploit in May 2026, and stressed that the protocol is permissionless by design.
Critics such as GoPlus argue that THORChain nodes can coordinate and halt signing. Supporters like Michael Perklin say neutral tools should not be blamed for how people use them. This is a protocol-design debate, and both sides make serious points.
Source: Official Post
THORChain Volume and Fees Surge
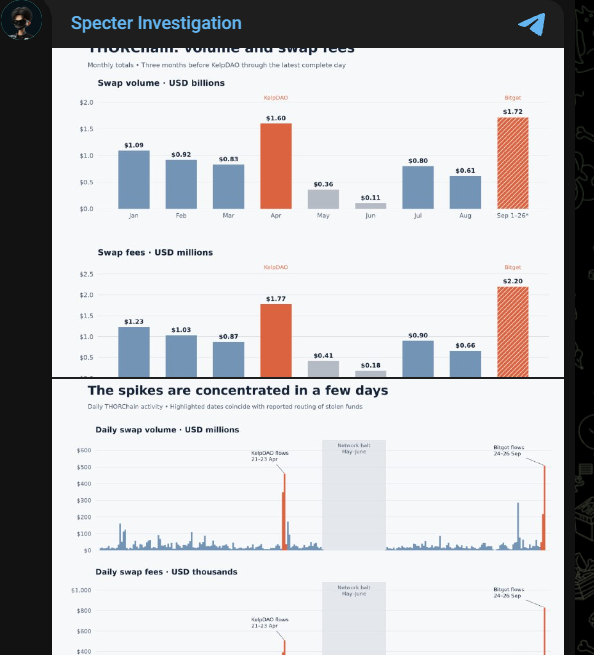
According to data shared by investigator Specter and reported by Wu Says, activity on the network spiked while the funds moved between September 24 and 26.
-
Daily swap volume topped $500M at one point.
-
Daily fees passed $800,000.
-
September swap volume reached $1.72B by September 26, with fees of $2.2M.
-
August volume was about $610M, with fees near $660,000.
A similar peak appeared in April, when stolen KelpDAO funds moved through the network. These numbers show total network activity. They do not equal the value of Bitget's stolen funds.
Bitget Withdrawal Update: Phased Resumption Begins
The latest Bitget withdrawal update is positive. The BTC withdrawals restarted on the Bitcoin network at 08:00 UTC on September 28, after extra security work on its withdrawal systems.
The vulnerability is fixed, and the incident remains contained. It reports no further unauthorized transfers since containment, and user account balances are unaffected. ETH, USDT, and other withdrawals will return gradually under the schedule announced earlier.
What Happens Next for Stolen Funds?
Bitget plans to publish a Bitget hack report with more technical detail. It says verified losses fall within its protection fund coverage, and it intends to refill the fund to the $300M baseline within one week.
Investigators are still following the stolen assets. The status of funds routed through THOR will stay a key part of that work.
Source: Specter Investigation
Bitget Hack Timeline
| Date | Development |
| Sep 24 | Bitget identifies the incident involving abnormal transfers |
| Sep 24 to 26 | Stolen funds move through THORChain; swap activity and fees spike |
| Sep 25 | Gracy Chen asks THORChain to refuse service to attacker addresses |
| Sep 26 | THORChain September swap volume reaches $1.72B |
| Sep 28 | Explanation of the attack method in a livestream |
| Sep 28, 08:00 UTC | Bitcoin BTC withdrawals resume |
| Coming days | Ethereum ETH, USDT and other withdrawals return; security report expected |
Conclusion
Three things define this crypto exchange hack so far: a credential-based attack that avoided private keys, stolen funds moving through THOR, and a steady recovery. The investigation and fund tracking are ongoing, so figures may change. Follow official channels for the next update.
Disclaimer: This article is for information only and is not financial advice. Cryptocurrency transactions and security incidents carry financial risk. Reported losses, fund movements, and recovery details can change as investigations develop. Always do your own research before making decisions.