Magic Eden NFT Exploit News: What Happened to 3832 Ethereum NFTs?
Magic Eden NFT Exploit: White-Hat Rescue Moves 3,832 NFTs to Safety
A wallet linked to a known Ethereum security researcher moved 3,832 NFTs out of hundreds of user wallets in the early hours of Friday, September 25, 2026.
The transfers are being described as a white-hat rescue rather than confirmed theft, with the activity tied to a suspected vulnerability in Magic Eden's former Ethereum marketplace contract. As of this writing, Eden has not publicly confirmed the cause or the full scope of the incident.
At a Glance
-
3,832 NFTs were transferred from hundreds of wallets in a single operation.
-
The assets were moved to an address beginning with 0x71cF.
-
Security researcher 0xQuit confirmed the operation was a white-hat rescue, not an attack.
-
Affected collections reportedly include Bored Ape Yacht Club, Azuki, and Mutant Ape Yacht Club.
-
Magic Eden has not confirmed the vulnerability's cause or impact.
Magic Eden NFT Exploit: What Happened?
NFT tracker CirrusNFT first spotted a single wallet pulling thousands of tokens from hundreds of separate addresses and initially raised alarm that a wallet-draining attack was underway. Minutes later, the transfers were linked to Magic Eden-related sales, each recorded at 0 ETH, meaning the tokens changed hands without any payment.
That pattern suggested an operator was using existing marketplace permissions rather than breaking into individual wallets. The activity was quickly reassessed as a likely white-hat operation, though the underlying cause remains unconfirmed by Magic Eden itself.
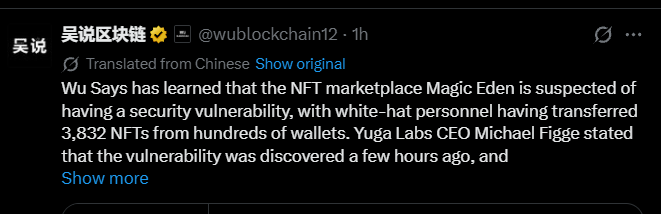
Source: Wu Blockchain
White-Hat Rescue Moves 3,832 NFTs to Safety
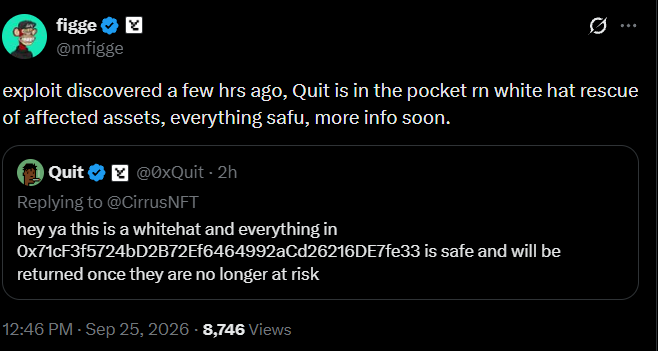
Security researcher 0xQuit, who also serves as Yuga Labs' vice president of blockchain, confirmed he controlled the wallet behind the transfers and said the assets were safe and would be returned once no longer at risk.
Yuga Labs CEO Michael Figge said the underlying exploit had been discovered only hours earlier and that further details were expected soon. The recovered NFTs are currently held at an address beginning 0x71cF3f5724bD2B72Ef6464992aCd26216DE7fe33. No return date or formal recovery process has been announced.
Magic Eden NFT Exploit: What Could Have Caused the Transfers?
Listing a crypto NFT on a marketplace typically requires signing an on-chain approval that lets the marketplace's smart contract move the token once a sale completes. Those approvals can remain active indefinitely unless a user manually revokes them, even after they stop trading.
Because Magic Eden shut down its Ethereum and Bitcoin marketplaces back in March 2026 to focus on Solana, some approvals from that earlier setup appear to have stayed live for months.
Available reporting points to these leftover permissions as the likely mechanism, but Magic Eden has not confirmed this explanation, and no official post-mortem has been released.
Source: Figge X Post
Timeline: From Detection to White-Hat Rescue
| Time (UTC) | Event |
| 06:31 | CirrusNFT flags a wallet moving NFTs from hundreds of addresses. |
| 06:35 | Transfers are linked to Eden-related NFT sales. |
| 06:42 | Thousands of NFTs sold for 0 ETH are flagged as potentially white-hat. |
| 06:47 | 0xQuit confirms the operation is a white-hat rescue. |
| Later | Yuga Labs CEO Michael Figge confirms an exploit was discovered, with more details expected. |
What Magic Eden Users Should Know
Anyone who previously listed NFTs on the Magic Eden Ethereum marketplace should check and revoke unused approvals through a tool like revoke.cash, and review recent ERC-721 transfers on Etherscan for unfamiliar activity.
Security researchers have also warned against signing any unexpected transaction claiming to "return" or "claim" rescued assets, since phishing attempts commonly follow public rescue events.
Third-party recovery bots should be treated as unsafe until an official return process is announced. Importantly, nothing so far suggests every crypto user has been affected.
What Remains Unknown?
Several details are still unverified: the exact vulnerable contract, a confirmed technical root cause, a full list of affected wallets, an independently verified dollar value of the assets, whether all transfers stemmed from one coordinated operation, and whether copycat attackers could exploit the same leftover approvals. It has not issued an official statement.
Conclusion
What can be confirmed is that 3,832 NFTs moved out of hundreds of wallets tied to a suspected flaw in an old Ethereum contract, and that 0xQuit says the assets are being held safely pending return.
The technical cause, full scope, and formal recovery timeline remain unconfirmed. Users are advised to follow official channels rather than acting on unofficial recovery claims.
YMYL Disclaimer: This article is for informational purposes only and does not constitute financial or security advice. Readers should independently verify any security steps and rely on official communications from official Posts before taking action involving wallet permissions or NFT assets. Cryptocurrency and NFT markets carry significant risk.