Binance iOS Vulnerability: Can an App Read Your Seed Phrase?
Binance iOS Vulnerability: Can an App Read Your Seed Phrase?
As of November 10, 2026, a new Binance iOS vulnerability alert is spreading in crypto news today.
Binance warns iPhone users that a flaw named worse_query lets a malicious app read local files from other apps.
Per Binance’s official post on X, the exposed data could include seed phrases, private keys and login credentials.
The exchange said this is a system-level issue and not unique to its platform.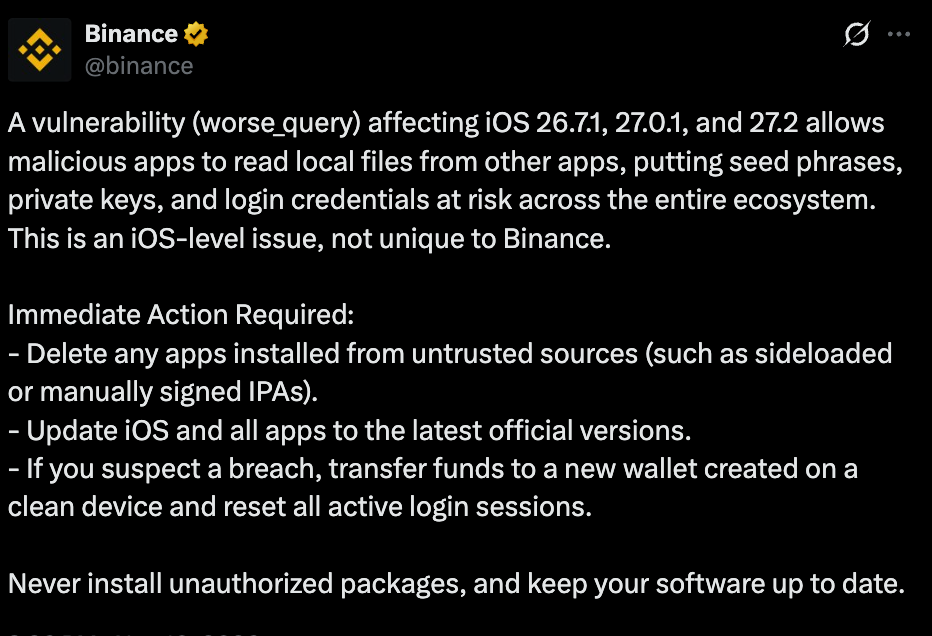
What Is worse_query Vulnerability?
SlowMist, a blockchain security firm, calls the worse_query iOS vulnerability a sandbox escape, not a jailbreak.
Its SlowMist iOS alert on X describes an iOS sandbox escape with a public proof-of-concept, framed as an iOS 0day exploit, and names bad_query as the earlier version.
It breaks the rule that apps cannot see each other, so a malicious app could reach and modify other apps’ data.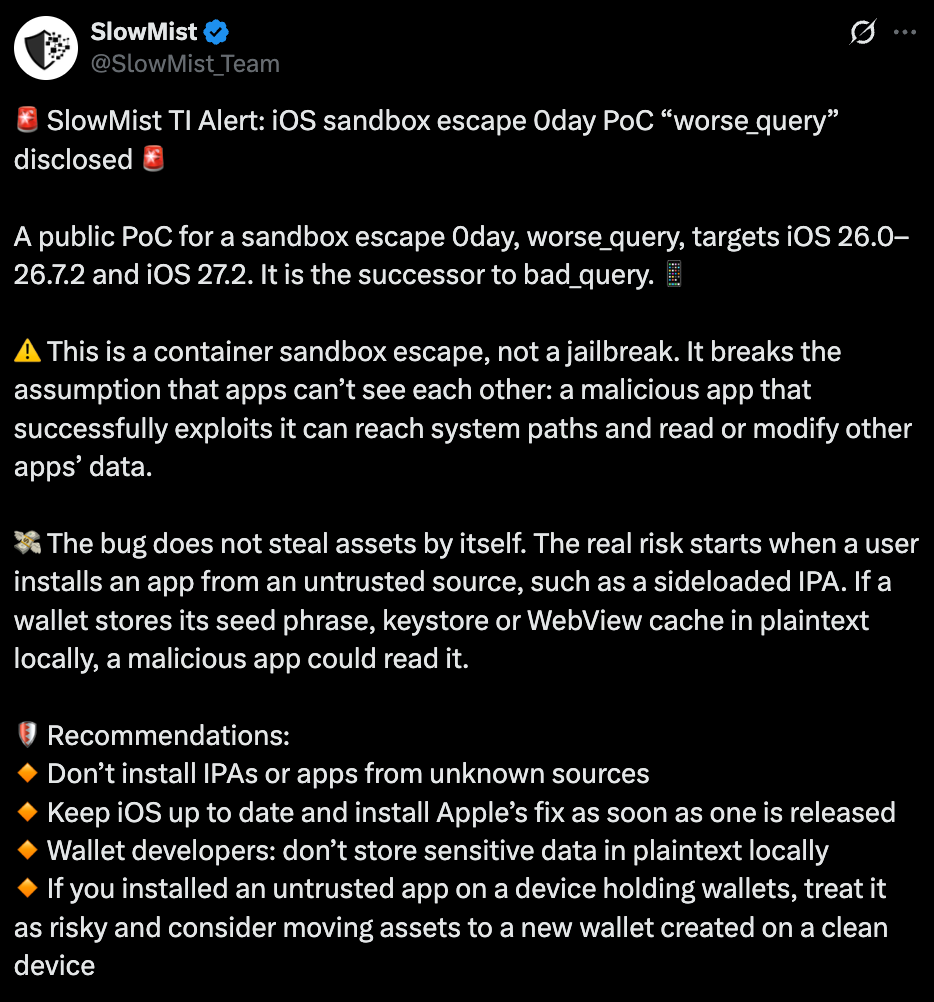
Which iOS Versions Are Affected by worse_query?
Source | Versions listed |
Binance | iOS 26.7.1, 27.0.1, 27.2 |
SlowMist | iOS 26.0 to 26.7.2 and 27.2 |
The Binance iOS vulnerability notice and the SlowMist post list different builds, so each range belongs to its own source. The iOS 27.2 vulnerability crypto holders discuss appears in both.
Can Malicious Apps Steal Crypto From iPhone?
Not on their own. SlowMist said the bug does not steal assets by itself, and the danger starts after a harmful install.
The sideloaded apps crypto wallet risk begins when a user installs an app from an untrusted source.
That sideloaded IPA risk rises if a wallet keeps its seed phrase, keystore or WebView cache in plaintext wallet storage.
In that case, an iPhone seed phrase hack becomes possible.
Crypto Banter also covered this news in its tweet on X, summarizing the Binance warning.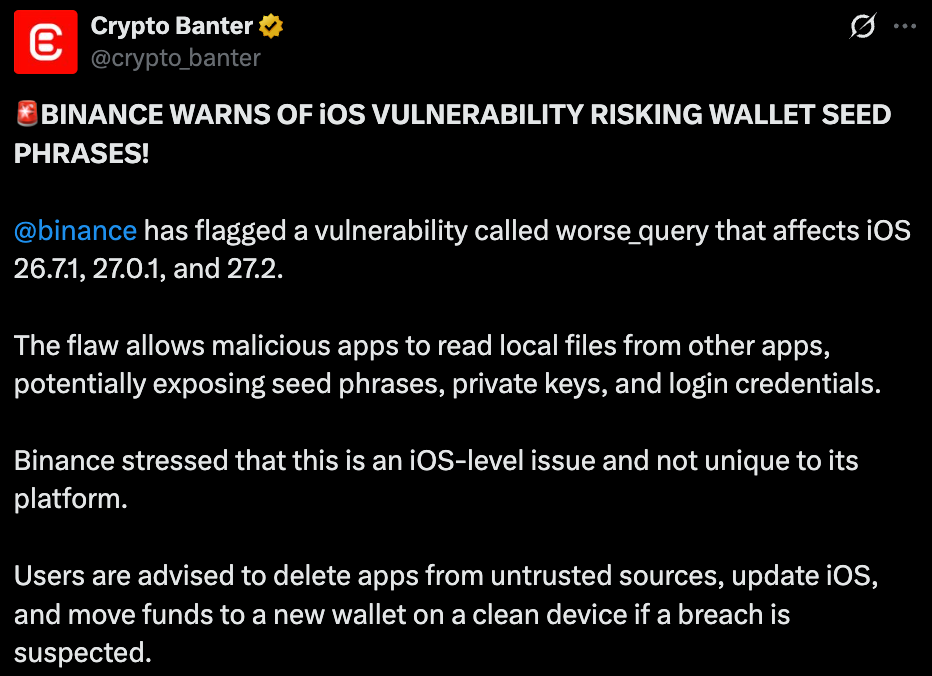
Is My Crypto Wallet Safe on iPhone?
The crypto wallet seed phrase risk depends on how each app stores secrets and what else runs on the same phone.
Is Binance App Safe on iOS?
Binance described the Binance iOS vulnerability as an Apple system problem, not a Binance one.
Apple published versions 27.2.1 and 26.7.3 on November 9, before both alerts, but Apple’s iOS 27.2.1 security notes do not name worse_query.
An Apple security patch for it is therefore unconfirmed, and SlowMist urged users to install Apple’s fix as soon as one arrives.
How to Protect Seed Phrase on iPhone?
Steps to protect seed phrase iPhone owners can take, per the Binance security alert and SlowMist:
Delete apps installed from untrusted sources
Update the system and all apps to official versions
Developers should avoid plaintext storage, per the SlowMist alert
Reset all active login sessions
Should I Move Funds to a New Wallet? iPhone Owners Ask
Both firms advise moving funds if a breach is suspected. SlowMist adds that any device holding wallets with an untrusted app installed should be treated as risky.
The Binance iOS warning today advises a clean device wallet, created on a device free of untrusted apps.
Expert View: What Could This Mean for Wallet Security?
Analysts tracking crypto news may read the Binance iOS vulnerability alert as a storage lesson, not a market event. Seed phrase security could depend less on the system and more on app design.
iPhone crypto wallet security may improve if developers encrypt local data. Private keys exposed through plaintext files remain the core concern.
Disclaimer: This article is for information only and is not financial, legal, or investment advice. Digital assets are volatile, and you can lose money. Verify details with official sources before making any decision.






