NEAR AI Security Breach: What Happened and Why Was Cloud Shut Down?
NEAR AI Security Breach: What Did the Team Confirm on November 10?
The NEAR AI Security Breach began when the team said it had identified unauthorized access to its internal systems. As a precaution, it paused NEAR AI Cloud inference while the investigation started.
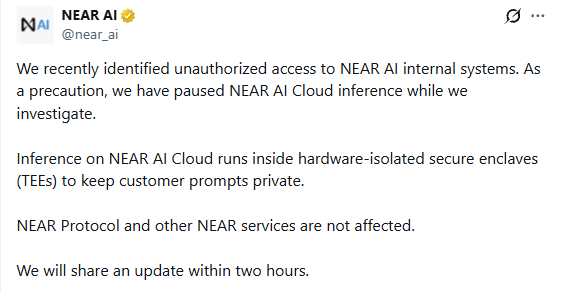
The announcement came in an official X post on November 10, 2026. The team added that NEAR Protocol and other NEAR services were not affected and promised an update within two hours.
That last line matters for token holders. The incident touched NEAR AI internal systems, not the base network.
Why Was NEAR AI Cloud Inference Paused So Quickly?
Pausing inference is a blunt step, but it limits risk while engineers check what was reached. NEAR AI Cloud runs customer prompts through AI models, so any doubt about system integrity affects every user at once.
The team said inference runs inside hardware-isolated secure enclaves, known as Trusted Execution Environments (TEEs). These are designed to keep prompts private, even from the operator of the machine.
The product is built around that privacy claim, which is part of the NEAR AI Cloud pitch. The team has not said whether any enclave was reached. The posts describe access to internal systems only.
How Did the NEAR AI Cloud Outage Unfold Through the Day?
The second update arrived within the promised window. The team said it had closed the unauthorized access and was completing its investigation. NEAR AI Cloud stayed paused until it could be restored safely.
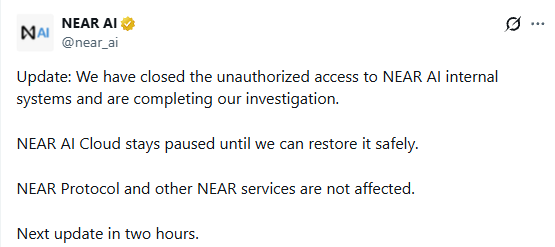
Source: NEAR AI Post on X
That wording separates two steps. Closing the access stopped the immediate problem. Restoring the service waited for a safe state.
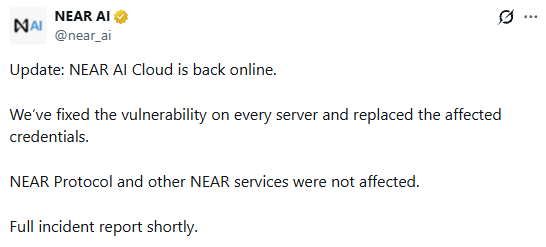
The third update confirmed the NEAR AI Cloud outage was over. The team said the service was back online, the vulnerability was fixed on every server, and the affected credentials were replaced. NEAR Protocol and other NEAR services were again described as unaffected.
NEAR AI Cloud Restored: What Is Still Unanswered?
The restoration notice, posted in a final X update, came with a promise of a full incident report shortly. Until that report is published, several points remain open.
How the unauthorized access happened
Which internal systems were reached
Whether any customer data or prompts were exposed
How long the access lasted before detection
None of these have been addressed in the public posts. Anything beyond the three updates counts as unconfirmed.
The replaced credentials hint at the likely scope of the cleanup. Rotating credentials is standard after access to internal systems, though the team has not said which ones were involved.
Expert Take: What Could Change the NEAR AI Security Incident Picture?
The data suggests a fast response. The pause, containment, and restoration all fit inside a single day, based on the three official posts.
The main uncertainty remains the full incident report. Its findings on cause, exposure, and the role of TEEs will shape how the market reads the event. For an AI cloud sold on privacy, that detail carries more weight than the speed of the fix.
Market impact on the NEAR token is not confirmed. The team has stressed that NEAR Protocol was untouched, and no verified price data links the incident to a move.
Conclusion
The NEAR AI Security Breach ended with the cloud back online, the vulnerability fixed, and credentials replaced.
The open questions on cause and data exposure now depend on the full incident report. More verified developments will appear in the crypto news today roundup.
Disclaimer: This article is for information only and is not financial advice. Crypto assets are volatile and carry risk, and security incidents can change quickly. Verify details with official sources before making any decision.






