Orbinum Network News: Private Vault Login Just Changed, Here Is Why
Orbinum Network News: Private Vault Ditches EIP-712 for SIWE
As of October 29, 2026, Orbinum Network news today centers on the Orbinum Private Vault SIWE login.
According to the official X post from October 28, 2026 (UTC), EVM wallets now unlock it only through Sign-In With Ethereum (SIWE), and EIP-712 is out of that flow.
The project’s own account also detailed the change in that post, which links a Medium explainer on the one-signature design.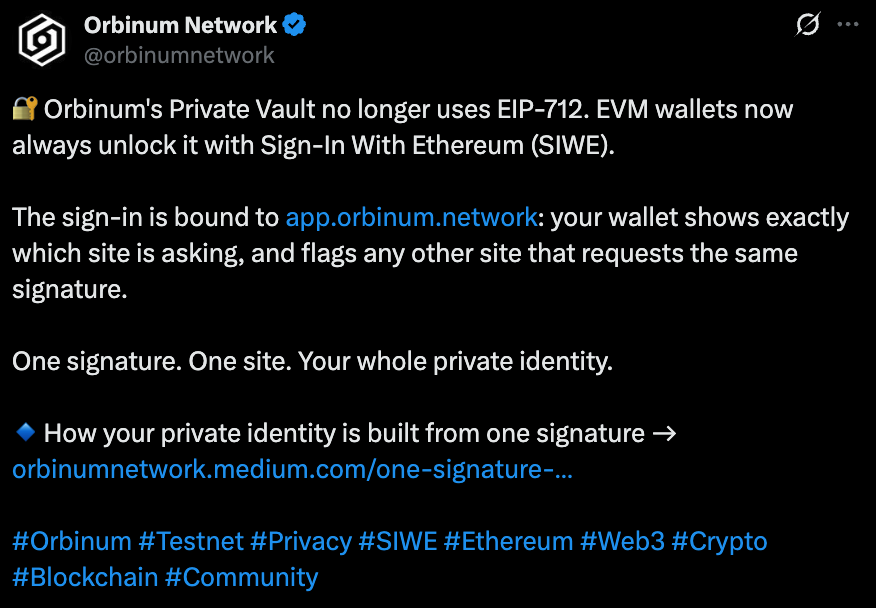
The Orbinum privacy blockchain is still on testnet, so this Orbinum Network update affects test users only. In crypto news today, login security rarely draws the attention listings do.
Orbinum Network News: What Changed in Private Vault Login?
The post makes four points:
-
EIP-712 is gone, so the Orbinum Network EIP-712 removed change is complete for EVM wallets.
-
All EVM users now follow the Orbinum SIWE flow.
-
Sign-in is bound to app.orbinum.network.
-
The wallet shows which site is asking and flags any other site requesting the same signature.
The team summed it up as “One signature. One site. Your whole private identity.”
That prompt names the requesting site, so this domain-bound sign-in acts as Orbinum wallet phishing protection. Orbinum wallet sign-in is now uniform.
What Is Sign-In With Ethereum SIWE?
Sign-In With Ethereum is the EIP-4361 standard for logging in with an Ethereum wallet through a structured message.
The message names the requesting domain, a chain ID and a nonce, so wallets can show which site is asking and users can spot phishing.
A SIWE wallet login replaces the earlier EIP-712 signature.
EIP-712 vs SIWE Difference: What Changes for Users?
PointEIP-712SIWE (EIP-4361)PurposeSigning typed structured dataStandard message for sign-inMessage fieldsDomain separator, typed fieldsDomain, chain ID, nonceStatus hereRemovedUsed for all EVM users
How Does Orbinum Private Vault Unlock Work?
Per the quick start guide, the app asks for a signed message the first time a user opens Wallet, then Shielded. That signature derives three keys:
-
The spending key, which moves notes
-
The viewing key, which decrypts them
-
A key that encrypts the local store
The guide says the signature is not a transaction, costs nothing and never leaves the browser. It is cached in encrypted form, so the Private Vault unlock prompt appears once per account.
The guide calls that signature the Orbinum private identity of a user. This wallet signature login works with MetaMask, per the guide.
Is Orbinum Private Vault Safe?
The guide does not call it risk free. It warns that a site tricking a user into signing the same message could derive the same keys and spend the notes, so users should confirm the domain first.
Orbinum Testnet Update: What Should Users Do?
For anyone following Orbinum Network News, the steps are short:
-
Confirm the domain reads app.orbinum.network before approving.
-
Use an EVM wallet on the testnet, chain ID 2700.
-
Claim testnet Orbinum ORB from the faucet, 5 ORB once per 24 hours.
-
Stop at any prompt that appears unexpectedly.
Expert View: What Could the Switch Mean?
Analysts following Orbinum Network News may read the change as a trust upgrade rather than a market event.
For a privacy-focused blockchain, the signing prompt is the most sensitive moment, since one signature derives every key.
A standard message gives wallets something concrete to check. Whether that cuts phishing losses can only be judged after wider testing. Readers tracking crypto news should note the post says nothing about mainnet timing or token details.
Disclaimer: This article is for information only and is not financial, legal, or investment advice. Investing involves risk. Verify details with official sources.









