Autonomous AI Cyberattacks: Google Warns of Machine-Speed Threats
Autonomous AI Cyberattacks How Google Found Hackers Exploiting Patches
Imagine a hacker who never sleeps, never takes a weekend off and works at machine speed.
That is the picture behind a warning from Felix Fan, CEO of Trust Wallet, who says most companies are not ready for autonomous AI cyberattacks.
His message links to the latest threat research from the Google Threat Intelligence Group, known as GTIG.
What Felix Fan Said
Fan shared a personal concern. He wrote that he is “paranoid” that the majority of companies are not prepared for this new era of attacks.
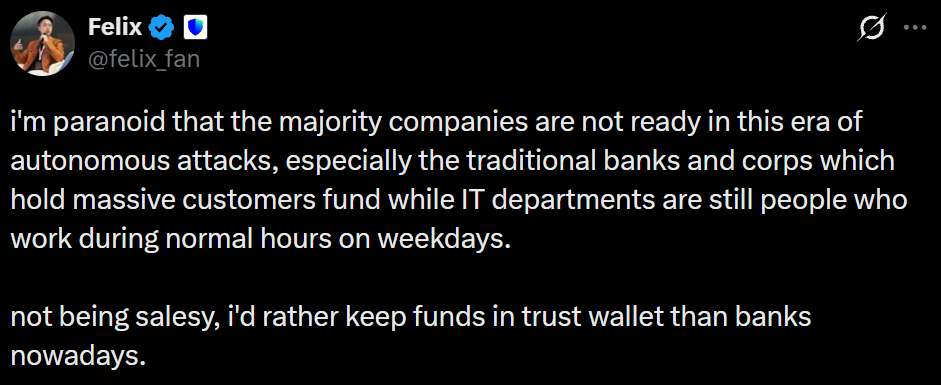
Source: Felix Fan Post
He singled out traditional banks and large corporations that hold huge amounts of customer money.
His reasoning is practical. In his words, the IT teams at such organizations often still consist of people who work normal hours on weekdays.
He added that he would rather keep funds in Trust Wallet than in banks nowadays, while saying he did not intend to sound salesy.
Two points are worth keeping in mind:
It is an opinion: the statement is the view of one executive, not a finding from the research.
No comparison data: his message does not include figures comparing losses at banks and crypto wallets.
What the Report Says About Autonomous AI Cyberattacks
Fan’s warning links to the official Google update published on November 16, 2026. It describes the newest edition of the group’s tracker report.
According to that update, attackers are now using autonomous LLM frameworks to continuously scan software updates, work out which flaw was patched and build an attack for it, all without human involvement.
Item | Detail |
Publisher | Google Threat Intelligence Group (GTIG) |
Post date | November 16, 2026 |
Report | AI Threat Tracker, full text on the Google Cloud Threat Intelligence blog |
Main finding | Attackers use LLM frameworks to turn fixes into attacks without human involvement |
The update also makes a plain statement about the challenge. Defending against machine-speed threats at human speed is not feasible, it says.
How These Attacks Work in Simple Steps
The update describes a chain that a person once had to perform manually. With autonomous AI cyberattacks, software can do each step on its own:
Watch: the framework keeps scanning software updates, around the clock.
Understand: it works out which flaw an update fixed.
Build: it creates an attack aimed at that flaw.
Repeat: no human needs to be involved at any stage.
This explains why the speed gap matters. A software fix shows that a weakness existed.
If a company takes days to apply it, an automated system may already be working on the attack.
That is the situation Fan describes when he mentions teams that work only during office hours.
How Defenders Are Responding
The company says it is helping defenders rethink security in the agentic era through Google AI Threat Defense.
The goal is to continuously find and fix flaws before attackers can exploit them, and the update’s headline calls for security built for nonstop defense.
The service combines several parts:
Component | Role described |
Gemini and other frontier models | Models used to find and fix flaws |
Wiz | Context and prioritization |
CodeMender | Automated patching |
Mandiant | Security expertise |
This did not start in November. In a May 11, 2026 report update, the group said it had identified, for the first time, an attacker using a zero-day exploit it believed was developed with AI.
It added that its own counter discovery may have stopped a wide-scale attack. The company also described protections for Gemini, including classifiers, in-model safeguards, and disabling malicious accounts, plus agents such as Big Sleep and CodeMender.
What This Means for Crypto Users and Companies
Neither the Google update nor Fan’s message gives step-by-step advice for individuals, so it is best to stick to what both say clearly:
Speed matters: fixes need to be found and applied quickly, because attackers are watching updates.
Defense must be continuous: a security team that is active only during office hours faces a threat that never pauses.
Defenders have new tools too: the same technology is being used to detect and repair weaknesses.
Conclusion
Fan’s concern and the Google research point in the same direction: automated attackers are faster than human routines.
The Google update does not name banks or wallets as safer or riskier, so Fan’s comparison remains his opinion.
What both sources stress is that autonomous AI cyberattacks reward whoever reacts fastest, and that defenders need tools and processes that never switch off.
Disclaimer
This article is for educational and informational purposes only and is not financial or investment advice. Crypto assets are high risk, their prices can be very volatile, and you can lose some or all of your money. Always do your own research and consider speaking with a licensed financial advisor before making investment decisions.






