Flap DNS Hijacking: Is flap.cool Safe After the flap.sh Attack?
Flap DNS Hijacking: What We Know About flap.sh and flap.cool
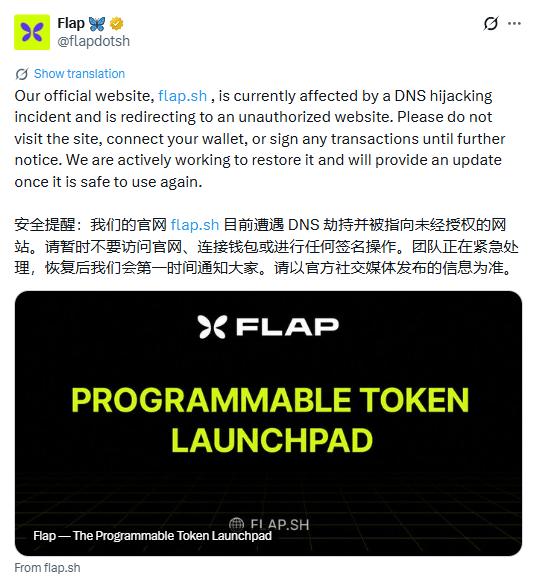
Flap says its official website, flap.sh, was hit by a DNS hijack and redirected visitors to an unauthorized site. The token launchpad told users not to visit, connect wallets or sign transactions. It later moved to flap.cool. This Flap DNS hijacking report separates confirmed facts from open questions as of October 31, 2026.
No confirmed loss figure was found. The root cause is still under investigation.
What Flap Has Confirmed So Far
Item | Flap's statement | Status |
flap.sh | DNS hijack, redirecting to an unauthorized site | Project-stated |
Advice | Do not visit, connect a wallet or sign | Active |
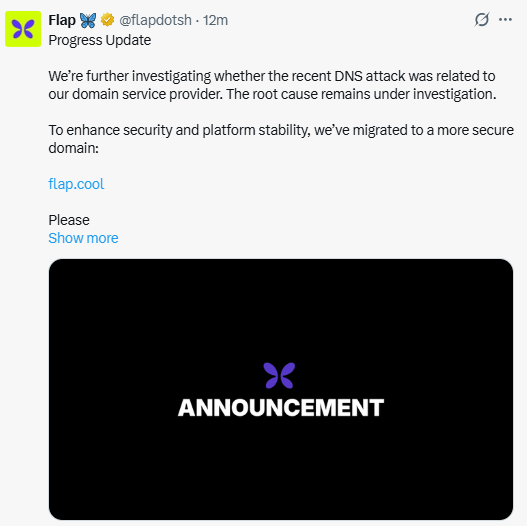
New domain | flap.cool | Announced on X |
Cause | A domain service provider link is being checked | Under investigation |
Losses | No figure published | Not found |
The project describes itself as modular token launch infrastructure. Reports place its first warning in the early hours of October 31 UTC. A security alert followed about 40 minutes later, per one report.
Flap says visitors to flap.sh will be redirected to flap.cool. It still advises opening flap.cool directly and avoiding flap.sh.
Flap's founder reportedly said the risk covers only users who visited the malicious site and connected or signed in the tens of minutes before the first warning. He also said that the project stores no private keys. Those posts were not independently fetched.
Reported Links to a Wider Attack Wave
Security firm Blockaid reportedly flagged an active front-end attack tied to the StepDrainer wallet-drainer toolkit. The alert named flap.sh, kintsu.xyz and stonkbrokers.cash. One report counts 12 sites.
Claim | Source | Status |
Flap DNS hijack | Flap | Project-confirmed |
Kintsu registrar-level hijack | Kintsu | Project-confirmed |
StepDrainer link | Blockaid alert, as reported | Not independently verified |
Shared registrar | None found | Not confirmed |
Kintsu told users who connected or signed after 00:00 UTC on October 31 to revoke approvals. Reported analysis also noted a newly issued TLS certificate and DNS results that differed from public resolvers. That analysis is unverified.
It is not confirmed that the DNS reports and the script reports describe one mechanism. A website attack does not change smart contracts. The platform has not reported a contract compromise, which was not independently checked.
Flap DNS Hijacking: What Users Should Check and Do Now
For anyone following this Flap DNS hijacking case, safety steps come first:
Open the domain only through links on its official X account
Check the spelling of flap.cool before connecting
If you signed on flap.sh on October 31, review token approvals on a revoke tool
Treat docs and contract lists hosted on flap.sh with care until restored
Ignore messages offering recovery or compensation
A DNS or front-end attack targets the website, not a wallet's keys. A drainer needs a signed approval to move tokens. Revoke tools list which contracts can spend your tokens. Whether any approvals were abused was not confirmed.
The Bottom Line
This Flap DNS hijacking review finds a project-confirmed website incident, a new domain and no published loss figure. Treat flap.cool as announced, not independently verified, and avoid flap.sh until the project confirms it is safe.
YMYL Disclaimer: This article is for information purposes only and is not financial, investment, or trading advice. Information is based on Flap's official X posts supplied, plus security alerts and project statements as reported, as of October 31, 2026. X and the flap.cool site were not independently fetched, and the root cause, loss figures and the StepDrainer link are unconfirmed. Statuses can change quickly. The safety steps are general guidance, not instructions from the team. No wrongdoing by the website is alleged or implied. Crypto assets are volatile and carry risk of loss, including full loss of funds. Always verify current details directly with official sources and consult a licensed advisor before making investment decisions.






