Chainalysis Security Breach: Agentic Attack Exposes User Data
What Happened in the Chainalysis Security Breach This Month
Crypto news today: Chainalysis has confirmed that an outside actor used “offensive agentic techniques” to reach its systems and internal tools. The Chainalysis security breach was detected this month, according to its customer notice.
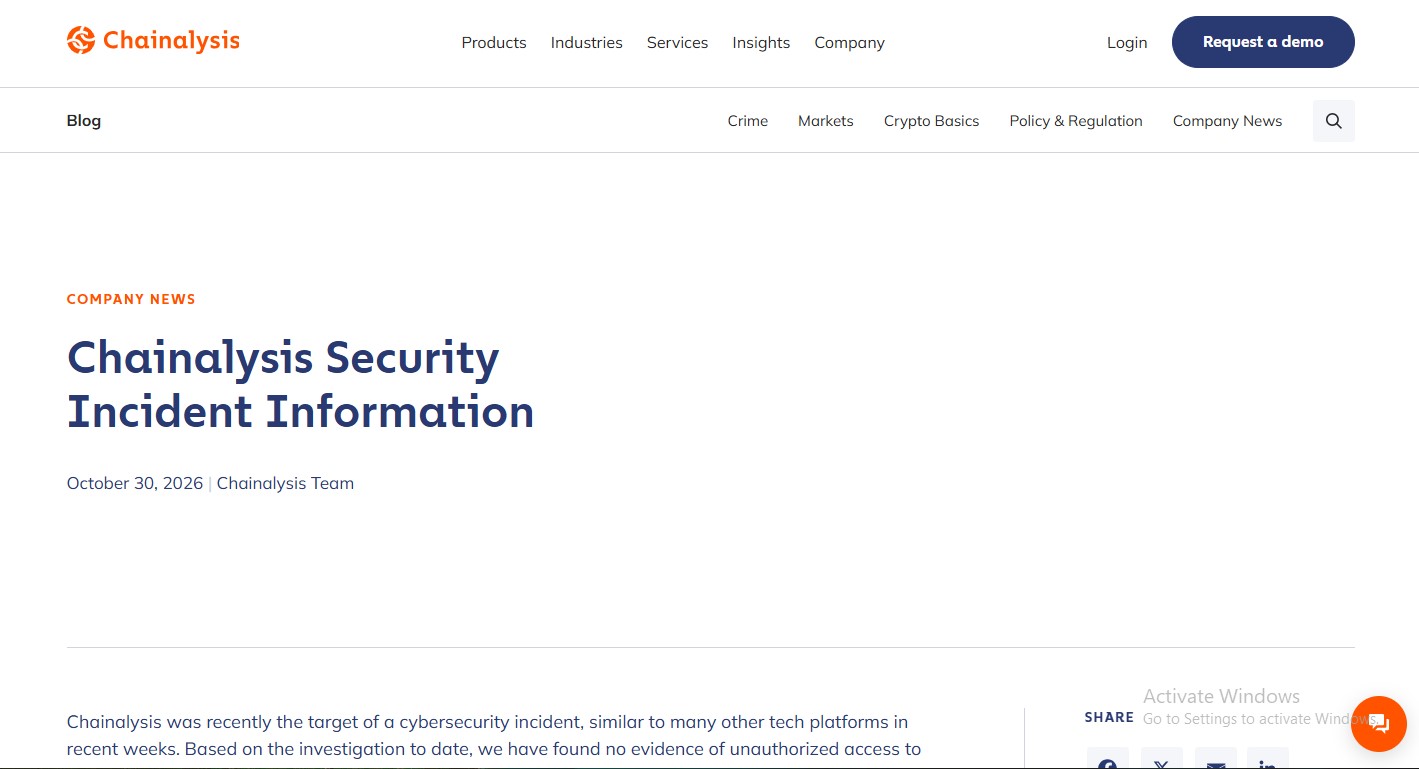
Chainalysis posted a short statement on its official blog on October 30, 2026, and sent a fuller notice to customers.
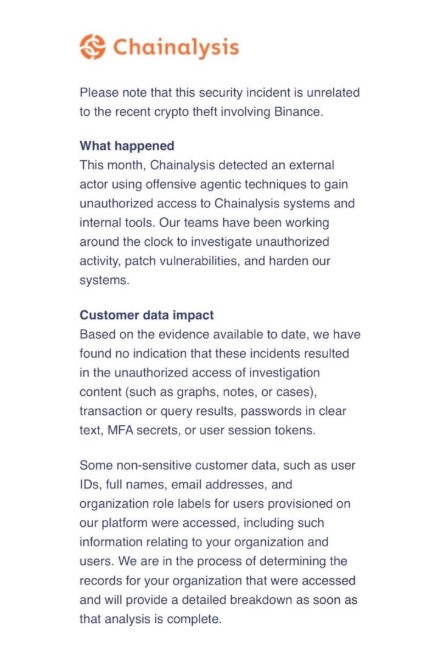
Source: Chainalysis Official Blog
The company says its teams are working around the clock to investigate the activity, patch vulnerabilities, and harden its systems.
What Customer Data Was Exposed and What Stayed Safe
The firm says only non-sensitive customer data was accessed. That covers user IDs, full names, email addresses, and organization role labels for users on its platform.
Data type | Status |
User IDs, names, emails, role labels | Accessed |
Investigation content (graphs, notes, cases) | No sign of access |
Transaction or query results | No sign of access |
Clear-text passwords, MFA secrets, session tokens | No sign of access |
These findings rest on the evidence available so far. The company is still working out which records belong to each organization and plans to share a detailed breakdown once that review ends.
Why the Agentic Attack Matters for Crypto Security
“Agentic” usually points to AI tools that can carry out tasks on their own. The notice does not explain how the attacker used them.
That makes the Chainalysis security breach notable. The firm builds tools for law enforcement agencies, exchanges, and financial institutions.
Even limited details can help attackers. Names, email addresses, and job roles can make phishing messages look more convincing. That is a general risk, not something the company has reported.
Recent incidents, such as the Keystone data breach, show why user data needs strong protection in crypto.
The firm also says the incident is unrelated to the recent Binance theft, which Bitcoin.com News put at about $6 billion. The Binance hack coverage tracks that separate case.
Company Update: Response and Steps Customers Can Take
The company says it is working with leading cybersecurity experts and has notified all customers. It promises more updates as the work continues.
Chainalysis also hosts a Trust Center for customers.
As a general step, users can turn on multifactor authentication for every account that offers it, as CISA advises. Unexpected login or password-reset prompts deserve extra caution.
What to Watch Next as the Security Review Continues
Key points to track:
The per-organization record breakdown the firm has promised
Any further customer updates
Whether more detail on the agentic method is shared
The Chainalysis security breach exposed basic account details, not investigation data, according to the company. The probe is ongoing, so findings may change. Stay tuned for more crypto security updates and the latest news on this story.
Disclaimer: This article is for educational and informational purposes only and should not be considered financial or investment advice. Always conduct your own research before making investment decisions.






