Gnosis Pay Data Breach: What Was Taken and What Comes Next?
Gnosis Pay Data Breach: Funds Safe, But Is Your Personal Data?
As of November 7, 2026, a card provider’s security incident is the standout item in crypto news today.
According to the company’s official blog post, an intrusion was detected on 3 November 2026, and the Gnosis Pay data breach exposed certain customer information.
Some users search for it as a Gnosis Pay hack, but the company calls it a data breach, not a theft of funds.
Gnosis Pay Data Breach: What Happened and What Was Exposed?
Gnosis Pay unauthorised access was flagged by its monitoring systems, and containment began within two hours, per the blog. The team then replaced the affected security credentials and fixed the vulnerability.
The hit system is the Gnosis Pay legacy system behind Gnosis Pay-branded cards, which the company calls its B2C business line.
Gnosis Pay customer data exposed in the incident is described only as certain information.
Each impacted user received an email with exact details, so no public list exists. It stresses that personal information exposed matters even when funds are untouched.
Gnosis Pay breach 3 November 2026: key dates
Date | Event |
3 November 2026 | Intrusion detected, containment within two hours |
6 November 2026 | Blog published, affected customers emailed |
20 December 2026 | B2C platform retirement |
The company also announced the incident in its official X post.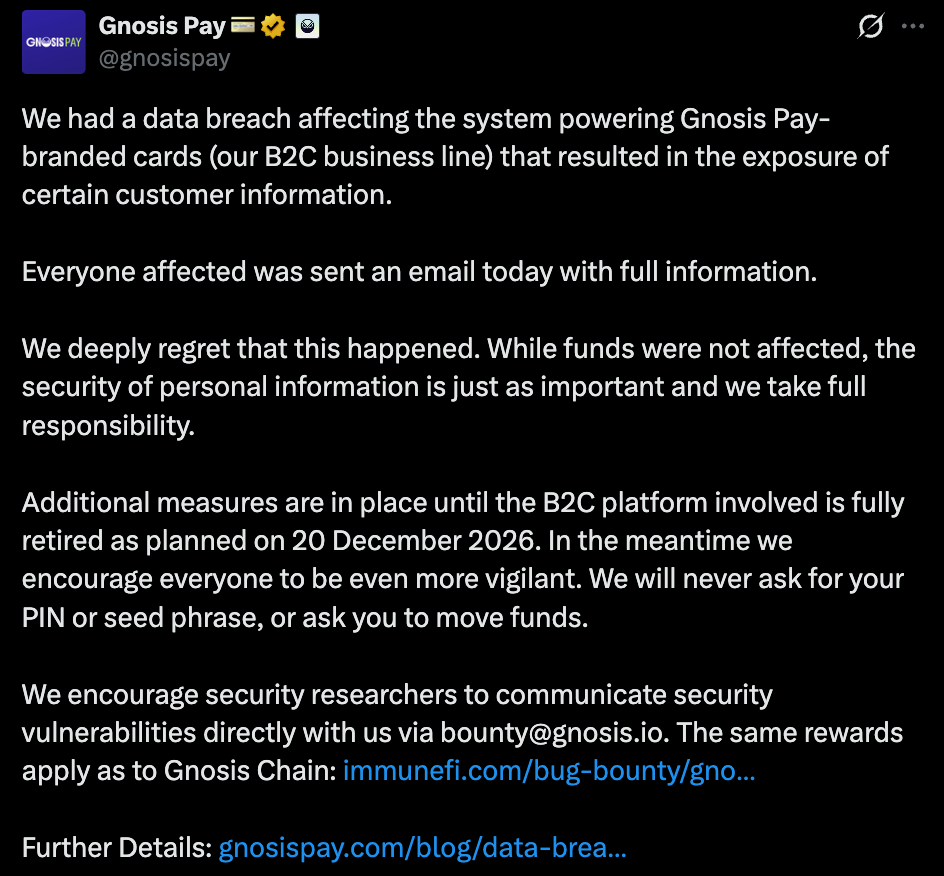
Is Gnosis Pay Safe After Data Breach?
Per the blog:
Funds: not affected, per the company
Enterprise platform not affected: it powers all white-label card programmes
Gnosis Pay card security now includes an extra step. Gnosis Pay 3D Secure mandatory online payments apply to every user, and the 3D Secure verification stays until Gnosis Pay B2C retirement on 20 December 2026.
The Gnosis Pay data breach was also reported to partners. It is in contact with data protection authorities and its card issuer Monavate, named in the blog footer.
Gnosis Pay Breach Email: What Does It Mean?
The blog says all impacted customers were emailed with exactly what was taken, and extra recommended actions depend on the data accessed.
Anyone worried can contact help@gnosispay.com, though directly affected users come first.
What to Do After the Gnosis Pay Data Breach?
How to protect crypto card after data breach:
Phishing warning: treat unexpected emails, texts or calls as suspicious, even with real details. Open the official web app directly.
Seed phrase and PIN safety: never share a seed phrase, private keys, PIN or full card number. The company will never ask users to move funds.
Keep your address and crypto holdings private.
Researchers can report flaws to bounty@gnosis.io, and the same bug bounty rewards apply as on its chain program.
GNO Price Today: CoinGecko Snapshot
CoinGecko data, as of November 7, 2026:
Metric | Value |
Price | $114.36 |
24h change | -0.6% |
24h range | $111.81 to $115.80 |
Market cap | $301.325M |
24h volume | $1.071M |
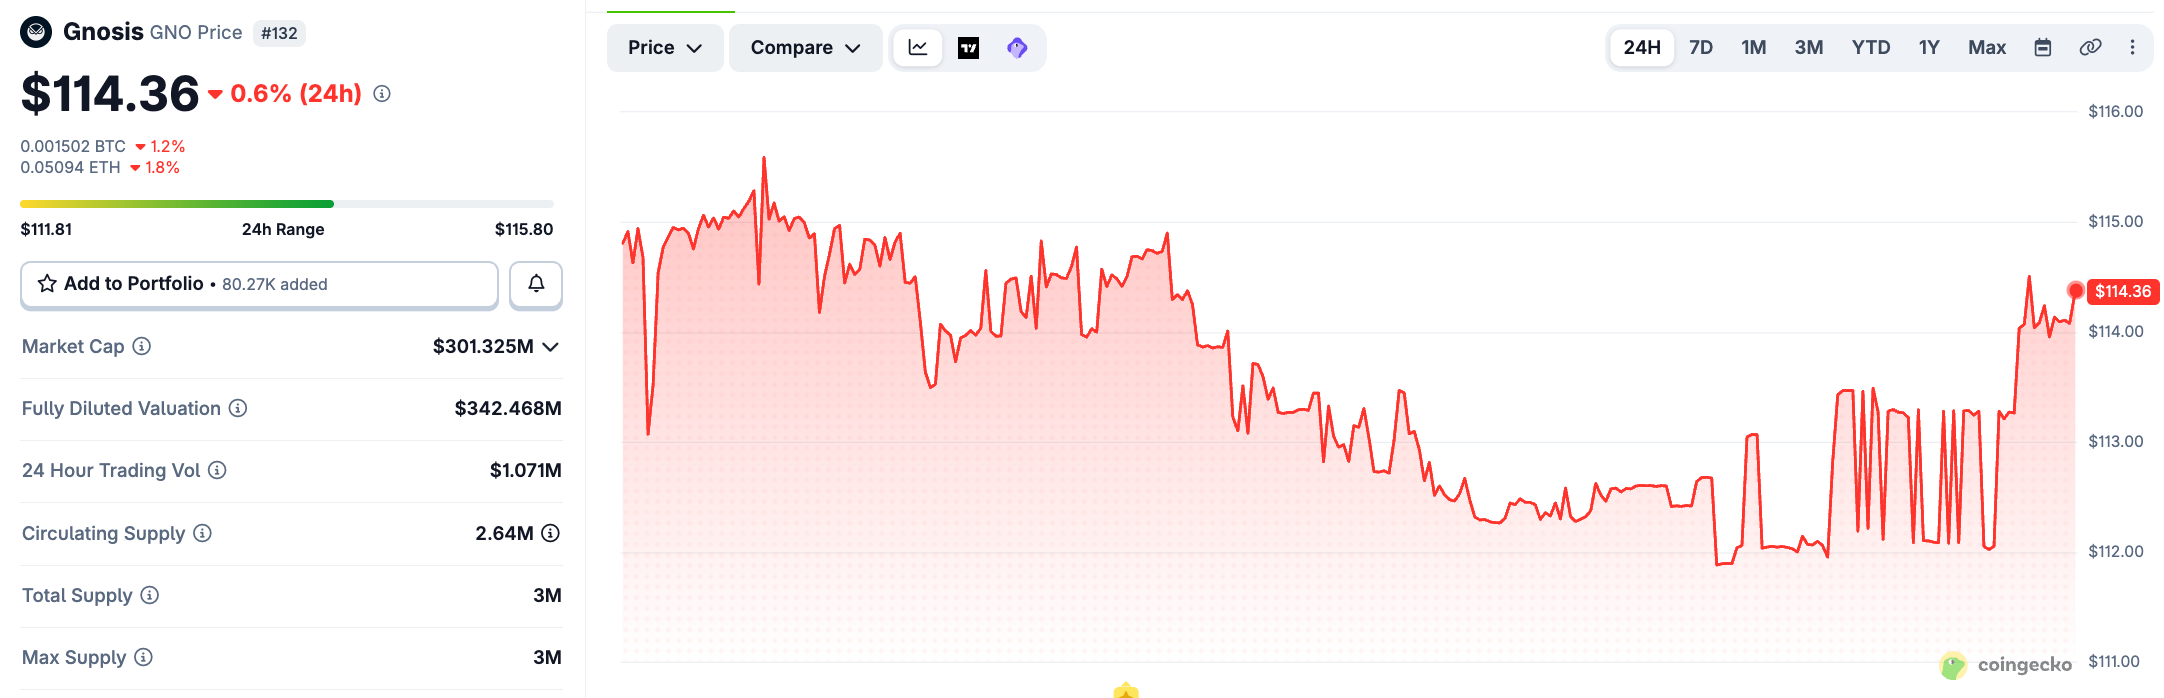
GNO is a token, not the card product, and the official statements do not mention it.
Expert View: What Could This Mean for Crypto Cards?
Analysts tracking crypto news may read this as a trust test for the sector rather than a market event.
Any crypto card data breach can raise phishing risk, even when funds stay safe.
Readers following Gnosis Pay news today should watch for company updates before the retirement date. Price impact, if any, remains uncertain.
Disclaimer: This article is for information only and is not financial, legal, or investment advice. Crypto assets are volatile. Verify details with official sources.






