Lighter Withdrawals Resume After API Key Leak, $5M USDC Returned
Key Takeaways
Lighter says deposits and withdrawals are back to normal after its Security Council turned off Guardian Mode.
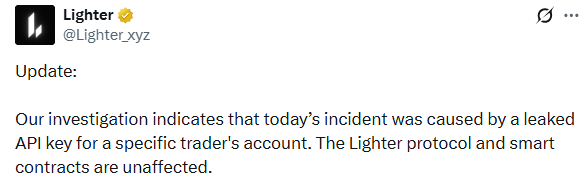
The team traced the incident to a leaked API key and says the protocol and smart contracts were not affected.
About 5 million USDC was returned to the affected trader, according to Lighter.
Lighter says the key leaked because the unsafe signing code reused nonces.
Lighter withdrawals resume after the exchange switched off Guardian Mode, the safety setting it used to pause payouts during a security incident on November 16.
Lighter says pending withdrawals are being processed and that about 5 million USDC went back to the affected trader. Here is what happened, how the leak worked, and what traders can do now.
Lighter Withdrawals Resume: Timeline of the Security Incident
Lighter first said on its official X account that it was investigating an incident involving a single compromised external party and that it had paused all withdrawals and pool creation as a precaution.
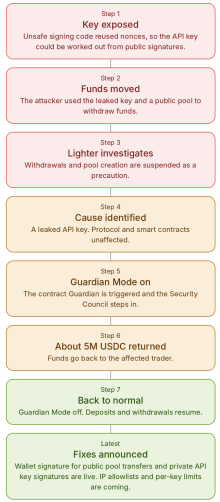
A later update said the cause was a leaked API key for one trader’s account, that the protocol and smart contracts were unaffected, and that Guardian Mode had been enabled to help recover funds from a further withdrawal attempt.
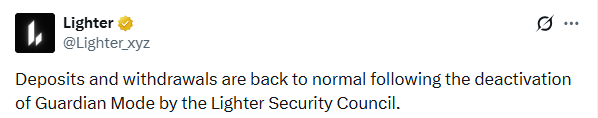
Lighter then confirmed that deposits and withdrawals were back to normal once the Security Council deactivated Guardian Mode.
Lighter API Key Leak Explained: How Nonce Reuse Exposed the Keys
Every transaction on Lighter is approved by a signature from an API key, and each signature needs a one-time random value called a nonce.
Lighter’s post-mortem says the affected accounts used signing code other than the official SDKs and that this code reused nonces. Because signatures are public, the team says an attacker could work out the private keys from public data without touching Lighter’s systems.
Lighter adds that the same math applies to Bitcoin and Ethereum signatures and that its official SDKs create nonces safely.
How the Funds Moved and What Lighter Recovered
According to Lighter, an API key can send funds to its own account’s subaccount, and a public pool counts as one. The team says the attacker created a public pool, minted shares in a separate account, moved the victim’s funds into the pool, and then redeemed those shares to withdraw.
Lighter’s smart contract Guardian detected the unusual activity and paused withdrawals, which let the Security Council return about 5 million USDC to the trader.
New Crypto Security Steps Lighter Is Adding
Lighter says it is adding IP allowlists so a key only works from a server you choose, plus limits for each key, such as which actions and markets it can use.
It is also watching signatures for nonce reuse, contacting affected accounts and voiding exposed keys.
Two changes are already live: moving funds into a public pool now needs a wallet signature, and API key signatures are no longer public.
How Traders Can Protect Their API Keys
Lighter advises traders to sign with an official SDK in Python, Go, TypeScript, or the Agent Kit.
Anyone using their own signing code should never build a nonce from a timestamp, a counter, or cached data and should keep keys out of code repositories. If you are unsure whether your code ever reused a nonce, the team suggests rotating all keys and switching to an official SDK.
Crypto Terms in Simple Words
API key: a digital key that lets software place trades on your account.
Nonce: a one-time random number added to each signature.
Guardian Mode: a smart contract safety mode that paused withdrawals during the incident.
Public pool: a shared account where other users can hold shares.
Risks to Keep in Mind
A leaked key can still cost money through bad trades or risky leveraged positions, so strong key habits matter even after the fix. With lighter withdrawals resume confirmed, the main lesson for traders is to use official SDKs and protect every API key.
The Bottom Line
Lighter withdrawals resume after the team switched off Guardian Mode, and the exchange says the incident came from a leaked API key, not a flaw in its protocol or smart contracts.
Traders should still use official SDKs, protect every API key, and rotate keys if there is any doubt about past signing code.
YMYL Disclaimer: This article is for information only and is not financial or investment advice. Crypto assets are volatile and carry a risk of loss. Check official sources before you act.






