MORE Markets Exploit Flow EVM Lending Bug Puts WFLOW Suppliers at Risk
MORE Markets Exploit: What Flow EVM's Bug Means for WFLOW Users Today
The MORE Markets exploit has hit a lending platform on Flow EVM, but the wider network is safe.
A bug in the platform’s own code let an attacker take out WFLOW tokens without repaying the matching debt.
The protocol is now paused, most users need to take no action, and everyone is warned to avoid fake recovery offers. Here are the verified details in simple words.
What Happened in the MORE Markets Exploit
According to the official Flow statement, the attack began at about 17:30 UTC on 16 November.
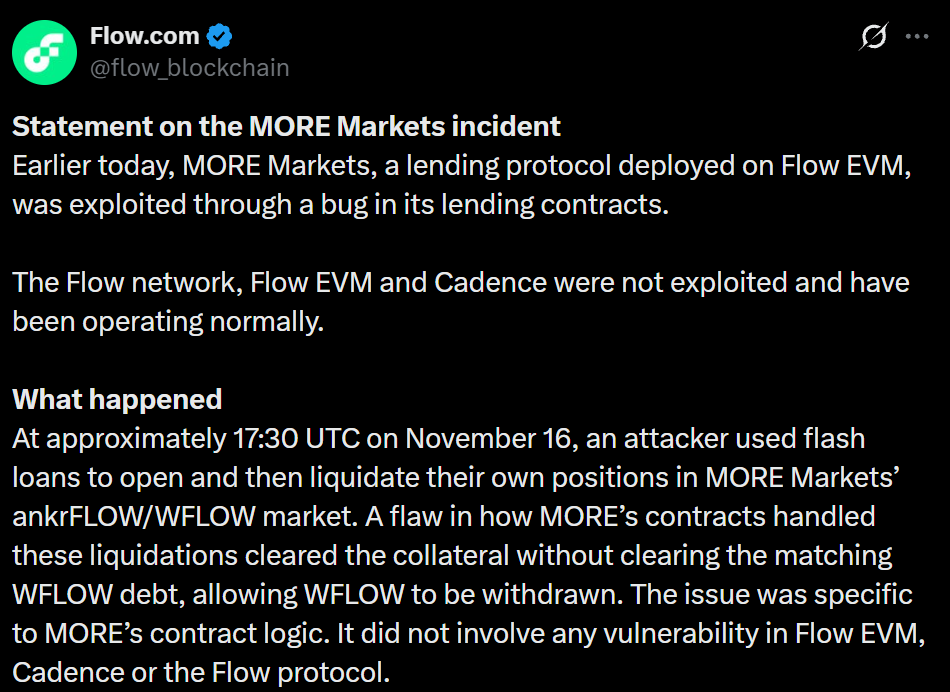
The attacker used flash loans, which are huge loans borrowed and repaid within a single transaction, to open positions in the ankrFLOW/WFLOW market and then liquidate those same positions.
Normally, a liquidation clears the collateral and the debt together. Here, a flaw in how the contracts handled liquidations cleared the collateral but left the matching WFLOW debt untouched.
Think of a shop that returns your security deposit without cancelling your loan. With the debt still sitting there, WFLOW-could be withdrawn.
The statement says the problem was specific to the platform’s contract logic.
Key facts at a glance:
Time: about 17:30 UTC on 16 November.
Where: the ankrFLOW/WFLOW market of a lending protocol on Flow EVM.
How: flash loans were used to open and then liquidate the attacker’s own positions.
Root cause: collateral was cleared without clearing the matching WFLOW debt.
Current status: the protocol is paused and an investigation is under way.
The Flow Network Was Not Exploited
The most important point for ordinary holders is what was not hacked. As per the same statement, the main network, Flow EVM, and the Cadence programming language were not exploited and have kept running normally.
The base network itself was not the target.
In other words, this was an application-level bug, not a break-in to the blockchain.
Steps Taken to Contain the Incident
The official update lists several actions:
The lending protocol has paused all activity.
Ankr has paused ankrFLOW as a precaution.
Security experts have been informed and are tracing the funds.
Foundation engineers are working with both teams to support the investigation and the fix.
Some exchanges temporarily paused FLOW deposits and withdrawals as a precaution. The foundation is in contact with them and expects services to resume shortly, though each exchange decides its own timing.
The statement thanks MORE, Ankr and other partners for responding quickly and helping contain the issue.
Who Is Affected and What to Do
The impact is limited to users who supplied to the ankrFLOW/WFLOW market on the platform. Everyone else is in a different position, as the table shows.
User type | Impact | What to do |
Suppliers of WFLOW in the ankrFLOW/WFLOW market | Directly affected | Wait for official updates |
Other users with positions on the platform | Not directly affected | No action needed now |
Holders of ankrFLOW | Not directly affected | No action needed now |
FLOW holders and traders | Network works normally; some exchanges pause. | Check your exchange for timing |
Positions cannot be changed while the protocols are paused, so there is nothing to fix on your side.
Scam warning: The foundation says not to interact with any site, token or account claiming to offer refunds or recovery.
Neither it nor the teams involved will ever ask for your seed phrase, private keys or funds.
Background: An Earlier Incident in August
This is not the first time these two projects have appeared together in a security notice.
In an official statement dated 1 September, the foundation described a different problem on 31 August.
A flaw in Ankr’s ankrFLOW staking contract let an attacker create about 8.6 million ankrFLOW with no backing.
The attacker used it as collateral to drain around 15.5 million WFLOW, worth about $410,000, from the lending platform. After slippage, the attacker realized about $246,000.
That statement said no depositor lost funds and promised to replace the drained WFLOW.
The causes are different: August involved a staking contract, while the latest MORE Markets exploit involves liquidation logic. This article makes no claim about any link between the two.
The latest statement does not give a loss amount, a repayment plan or a restart date.
Those details are expected from the teams’ official accounts, MORE DeFi and the AnkrLabs Team, which will also explain how affected users will be supported.
Conclusion
The MORE Markets exploit looks contained to one market on one application, with the main network working normally.
Affected suppliers should wait for official updates and ignore anyone offering refunds.
Until the teams publish their findings, treat any claimed numbers or timelines with care, and rely only on the official accounts for news about restarts, repayments, or support for affected users.
Disclaimer
This article is for educational and informational purposes only and is not financial or investment advice. Crypto assets are high risk, their prices can be very volatile, and you can lose some or all of your money. Always do your own research and consider speaking with a licensed financial advisor before making investment decisions.






