Top Hacker Groups in the World: 15 Threats Crypto Users Must Know
This guide to the Top Hacker Groups in the World is for readers who follow crypto news today and want to know the threats around wallets, exchanges, and blockchain projects.
The sections below explain each group in plain words and end with simple crypto security steps.
Top Hacker Groups in the World at a Glance: Key Takeaways
The list covers 15 cyber threat groups that public reports link to North Korea, Russia, China, Iran, and global crime networks. When it comes to crypto and finance, five names deserve the closest attention: Lazarus Group, APT38, APT41, Sandworm, and Scattered Spider.
North Korea is linked to Lazarus Group, BeagleBoyz, and Andariel.
Russia brings Fancy Bear, Cozy Bear, and Sandworm.
China adds APT41, Volt Typhoon, APT10, and Mustang Panda.
Iran is represented by MuddyWater and Charming Kitten.
The last three, Scattered Spider, FIN7, and LockBit, come from international or Eastern European networks.
Iran: MuddyWater and APT35.
International or Eastern Europe: Scattered Spider, FIN7, and LockBit.
A country link in this list does not prove that a government ordered every attack, since proof needs forensic evidence and checks by outside experts.
What Threat Groups, Ransomware, and Social Engineering Mean
Reports on the Top Hacker Groups in the World use terms that new readers may not know, so short meanings help.
APT: short for advanced persistent threat, a group that hides in a network for a long time.
State-sponsored: a group that public reports link to a government.
Ransomware: a type of malware that locks a victim’s files and asks for payment, often while threatening to leak the stolen data.
Social engineering: a trick where an attacker talks a real person, such as a help desk worker, into handing over access.
SIM swapping: a scam in which a thief moves a victim’s phone number to a new SIM card, so login codes sent by text land on the thief’s phone.
Supply chain attack: an attack that hides malware inside trusted software, which then reaches everyone who installs it.
North Korean Hacker Groups Targeting Crypto Exchanges and Banks
1. Lazarus Group
Among the top hacker groups in the world, Lazarus Group is the name most often tied to crypto theft. MITRE ATT&CK calls it a North Korean state-sponsored group, and it notes that reports often use the name for several teams, as shown on the MITRE ATT&CK page for Lazarus Group.
Public reports link the group to big crypto thefts, the Sony Pictures attack, and spying across the world.
2. APT38 (BeagleBoyz)
Banks, financial networks, and payment systems have been the main prey of BeagleBoyz, a group known for stealing large sums.
3. Andariel
Public reports list Andariel as a group that goes after defense firms, banks, and government bodies, mixing money-driven crime with spying.
Russian Hacker Groups Behind Espionage and Infrastructure Attacks
4. APT28 (Fancy Bear)
Fancy Bear is tied in public reports to spy work against governments, armies, NATO, and political groups.
5. APT29 (Cozy Bear)
APT29 is best known for the SolarWinds supply chain attack and has hit government agencies, tech firms, and research groups.
6. Sandworm
Sandworm focuses on energy systems, power grids, phone networks, and government networks. It is known for harmful attacks, including those on Ukraine’s power grid, and it is on the crypto watch list because damage to shared systems can stop the services that exchanges and node operators need.
Chinese Hacker Groups Focused on Espionage and Long-Term Access
7. APT41
APT41 stands out because public reports describe both spy work and attacks made for money, aimed at tech, health, telecom, and finance firms.
8. Volt Typhoon
Few groups on this list are as patient as Volt Typhoon, which is known for sitting quietly inside critical systems, telecom networks, and government networks for long stretches of time.
9. APT10 (Stone Panda)
Reports connect APT10 to the theft of trade secrets and business ideas from companies and tech firms.
10. Mustang Panda
Governments, political groups, and diplomats sit at the center of the spy campaigns tied to Mustang Panda.
Iranian Hacker Groups Using Phishing and Credential Theft
11. MuddyWater
Password theft and spying on government bodies, telecom firms, and providers of key services are the main activities reported for MuddyWater.
12. APT35 (Charming Kitten)
APT35 uses phishing against officials, scholars, and reporters.
International Groups Using Ransomware and Social Engineering
13. Scattered Spider
Scattered Spider is the group most tied to company help desks. A joint advisory from the FBI and CISA says it targets large firms and their IT help desks and is expert at social engineering, with full details in the CISA advisory on Scattered Spider.
14. FIN7
FIN7 is known for payment card theft from stores, hotels, and payment firms.
15. LockBit
Data theft comes first with LockBit, a ransomware group that then demands payment from businesses, hospitals, and government agencies.
Five Top Hacker Groups in the World to Watch in Crypto and Finance
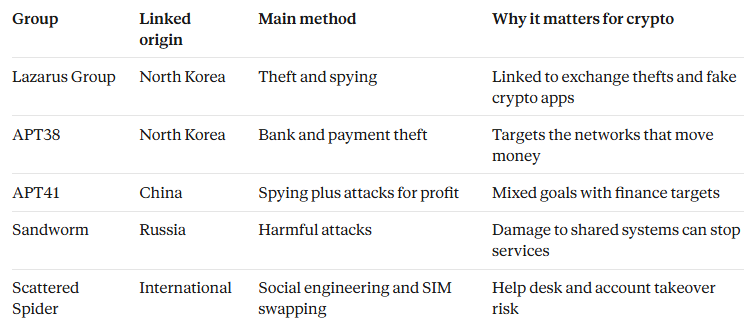
As of October 30, 2026, group names, links, and tactics can change as new reports appear, so the latest details are best checked on official advisory pages.
How Crypto Users Can Reduce Risk From Cyber Threat Groups
Most readers will never face one of the Top Hacker Groups in the World directly, yet the same tricks reach normal wallets through fake links, fake apps, and phone number theft. A few habits close most of those doors.
Keep seed phrases offline and never type them into a website or share them with support staff.
Use an authenticator app or a hardware key instead of SMS codes, since SIM swapping targets text messages.
Install wallet and trading apps only from official stores and project sites, because fake crypto apps are a known way to spread malware.
Check every claim page against a project’s verified accounts, as explained in this guide to spotting a fake crypto airdrop.
Turn on withdrawal address whitelists and login alerts for exchange accounts.
The same CISA and FBI advisory recommends sign-in that resists phishing, offline backups, and app controls for companies, which gives exchanges and crypto firms a useful base. More background is in this [crypto exchange hack prevention guide](insert CoinGabbar URL).
Final Verdict: What the Top Hacker Groups in the World Mean for Crypto
The top hacker groups in the world do not threaten crypto in the same way. North Korean groups are tied most to theft from exchanges and banks.
Scattered Spider shows how one help desk call can open a company network, and groups such as Sandworm and Volt Typhoon raise wider risks for services that crypto relies on.
For single holders, the rule is to guard the phone number, the seed phrase, and the download source first. For exchanges and projects, the focus is staff training, sign-in that resists phishing, and a clear plan for incidents. Names on a list matter less than habits, since most losses start with one careless click.
Disclaimer: This article is for educational and informational purposes only and should not be considered financial or investment advice. Country links do not prove that a government controls every attack, and proof needs forensic evidence. Readers are advised to do their own research.