Trezor Data Breach: 27,000 Customers Exposed, Is Your Crypto Safe?
Trezor Data Breach: 27,000 Customers Exposed, Is Your Crypto Safe?
As of November 17, 2026, crypto news today starts with a Trezor data breach traced to delivery partner Skladon.
In an official X post on November 16, 2026 at 16:18 UTC, the company said an attacker had gained unauthorized access to order data there.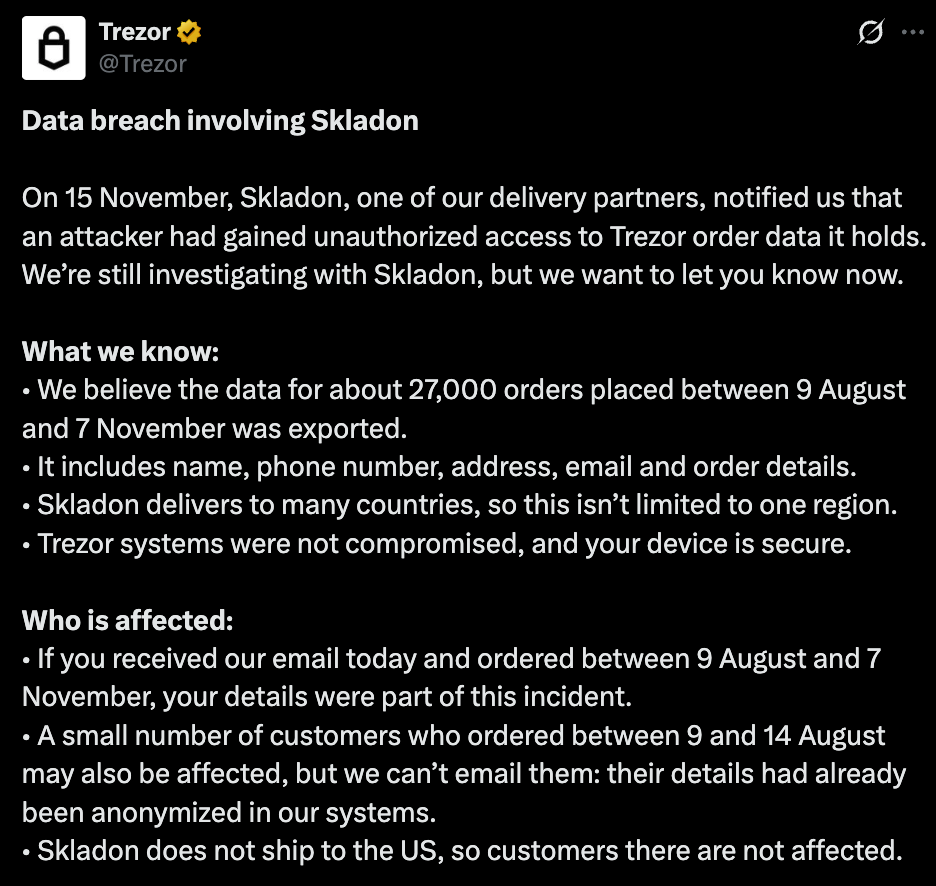
The Trezor Skladon breach occurred on November 7, and the partner alerted the company on November 15, according to the official blog post.
Trezor Skladon Data Breach Explained: What Happened?
The Skladon logistics partner network was breached on November 7, 2026, exposing shipping records tied to roughly 27,000 orders.
The wallet maker believes the attacker exported the records, and says its own systems were not compromised. The investigation is ongoing.
Detail | Reported |
Breach date | November 7, 2026 |
Company alerted | November 15, 2026 |
Orders affected | About 27,000 |
Order window | August 9 to November 7, 2026 |
Wu Blockchain also covered this news in its tweet on X, noting customers in several countries were hit, but not those in the US.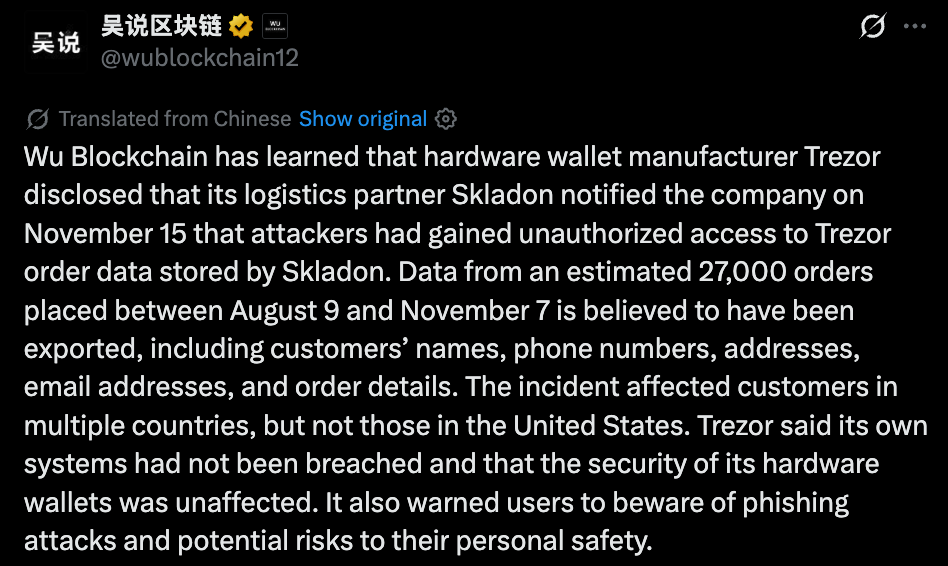
Trezor Customer Data Leak 27,000 Orders: What Was Exposed?
The Trezor breach 27000 orders figure is an estimate. The order data exported includes this customer personal data:
Full names
Phone numbers
Delivery addresses
Email addresses
Order date, product name and price
Wallet backups, PINs and passphrases were not involved, since neither company holds them.
Was My Trezor Data Leaked? Who Is Affected?
Anyone who received the email and ordered between August 9 and November 7 was part of the incident.
A few buyers from August 9 to 14 may also be affected, but their records were already anonymized, so no email was possible.
Is Trezor affected in US after breach? No. The X post says Skladon does not ship there, though it delivers to many other countries.
Is Trezor Safe After Data Breach?
The company says devices remain secure. The Trezor data breach exposed personal details, not keys, so hardware wallet security holds and cold wallet funds were untouched.
Trezor Order Data Leaked: What to Do?
This Trezor phishing warning matters because scammers may quote real order details, and some customers already reported scam calls, per the blog.
A phishing attack can also arrive by post. How to protect crypto after hardware wallet data breach:
Treat unexpected calls, texts, emails or letters as suspicious
A Trezor email scam may quote what you bought
Contact the official support page only
Seed phrase safety: never share it, enter it only on the device
Physical security risk: call local police if threatened
Trezor Anonymous Pickup: How It Works?
It is live in 18 European countries. Buyers collect parcels from a locker or pickup point, so name and home address never reach the company. A US launch is planned.
Trezor data retention 45 days replaces the old 90-day data retention period, with further cuts planned.
BTC Price Today: CoinGecko Snapshot
CoinGecko data, as of November 17, 2026:
Metric | Value |
Price | $64,844.94 |
24h change | +0.3% |
7d change | -12.7% |
Market cap | $1.304T |
The Trezor data breach has no stated link to these moves. Readers following crypto news can monitor it there.
Expert View: What Could This Breach Mean?
Analysts watching crypto wallet users may read this delivery partner breach as a supply chain lesson, since the weak point sat outside the device. Physical risk could now rival phishing.
Shorter retention may limit exposure, but exported records cannot be recalled. Will the Trezor data breach move prices? Unclear.
Disclaimer: This article is for information only and is not financial, legal, or investment advice. Crypto assets are volatile. Verify details with official sources.






