Chainlink Confidential Compute: 1M Runs in Just 30 Days
Chainlink Confidential Compute: How Did It Reach 1M Runs in 30 Days?
Public blockchains show everything to everyone, which is a problem for banks and funds that must protect client details.
Chainlink Confidential Compute is built to solve that gap, and a new AWS case study shows how early access went: about 1 million workflow runs in roughly 30 days, covering more than 170 different use cases.
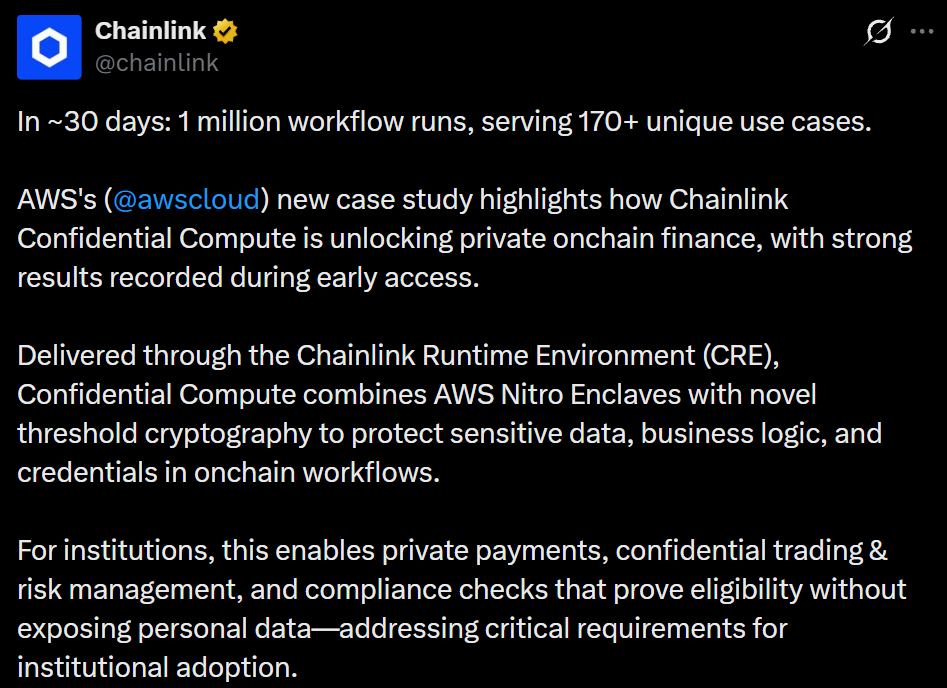
Source: Chainlink Post
Why Public Blockchains Struggle With Sensitive Information
Public blockchains are open by design. Every transaction and contract can be seen by anyone, so business logic, client details and login credentials can be exposed.
The case study explains that this can lead to financial losses, legal and licensing risks, and damaged trust between firms and their clients.
Chainlink Labs, one of the primary contributing developers of the network, sees this lack of secrecy as a major barrier to institutions using onchain finance and tokenization (turning real-world assets into digital tokens).
What the Early Access Numbers Show
The results for Chainlink Confidential Compute come from its early access phase:
Metric | Result |
Workflow runs | 1 million |
Time period | About 30 days |
Unique use cases served | 170+ |
Simple maths puts that at roughly 33,000 runs a day on average. A workflow is a set of automatic steps that connects blockchains with outside systems, such as a bank’s records or a price source.
The same page notes that developers tried ideas beyond what the team first planned, and it links this to the flexible, modular design of the Chainlink Runtime Environment (CRE).
In other words, builders found uses the creators had not imagined, which is often a healthy sign for a new tool.
How the Technology Works
Chainlink Confidential Compute is delivered through CRE, which coordinates workflows across blockchains, company systems, APIs and AI models.
In plain terms, it works like this:
Sealed rooms: Work runs inside AWS Nitro Enclaves, isolated computing spaces on Amazon EC2 that come with a cryptographic check of what is running inside.
Split keys: Sensitive items, such as API passwords, are stored in a Vault network using threshold encryption. Access is divided among independent node operators, so no single operator holds the full secret.
Release only after checks: Nodes hand over their pieces only after authorization and remote attestation checks. The sealed room rebuilds the secret, runs the workflow, then discards the secret.
Custom build: The same team wrote its own WebAssembly runtime for the enclave, plus the logic that links it to the CRE workflow engine.
The team picked this setup for its ease of development and strong security, and because AWS services were already part of its stack.
Its researchers also say no cryptographic alternative matched it on time to market and computing speed.
Under AWS’s shared responsibility model, this setup can protect confidential logic, secrets and proprietary information from access by any single party, including the lab itself.
Real-World Uses Explained Simply
The case study lists private payments, confidential risk management, and privacy-preserving compliance as supported use cases.
The official product announcement adds more detail:
Use case | What stays private |
Market-data sharing | Licensed index figures reach approved subscribers only |
Private transactions | Amounts, counterparties and positions |
Tokenized bonds, private credit and fund shares | Investor details, deal sizes and pricing terms |
Identity and compliance checks | Personal details; only a result, such as yes or no, goes onchain |
The announcement also says each confidential workflow produces cryptographic proof of what was run, and extra details in that proof can be encrypted for an auditor or regulator.
That matters because institutions need privacy and accountability together.
Rollout Plan and What to Keep in Mind
The original announcement from November 4, 2025 said early access would arrive in early 2026, with general access planned for later in 2026.
Readers should check Chainlink’s official pages for the current status, as the case study describes only the early access period.
Three points are worth remembering:
The first design relies on trusted execution environments, which the announcement says need extra safeguards against possible hardware weaknesses.
Future versions may add other privacy methods, such as zero-knowledge proofs, secure multiparty computation and fully homomorphic encryption.
The 1 million figure counts workflow runs, not money moved or number of customers.
Conclusion
Chainlink Confidential Compute aims to let institutions use sensitive information on-chain without putting it on public display.
The early access numbers show strong developer interest, with 1 million runs and over 170 use cases in about a month.
The next test is how it performs once general access opens to everyone.
Disclaimer
This article is for educational and informational purposes only and is not financial or investment advice. Crypto assets are high risk, their prices can be very volatile, and you can lose some or all of your money. Always do your own research and consider speaking with a licensed financial advisor before making investment decisions.






