Polymarket Security Breach: Hackers Drain $2.7M via DebugBear
Polymarket Security Breach News: What Happened on October 29
The latest crypto news from October 29 shows a Polymarket security breach on the international site, Polymarket.com. A compromised third-party provider let attackers drain funds from some user accounts. Trading stopped for about one hour before it resumed. The U.S.-regulated platform was not affected.
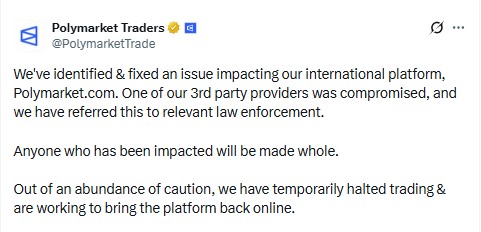
Source: Polymarket Traders X-Post
This update rests on the company’s status page and its official X account. The problem sat on the client side, inside a third-party script. It was not a flaw in the core smart contracts or the trading engine. Both points come from official updates posted on October 29, 2026.
How a Third-Party Script Let Attackers Reach User Wallets
The exchange has not named the provider. People familiar with the matter told CNBC and NBC News it was DebugBear, a UK-based website performance tool. Its real user monitoring (RUM) product loads a JavaScript snippet on a site.
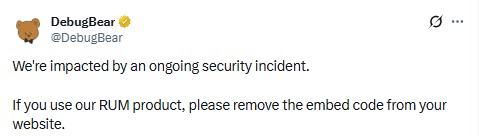
DebugBear posted on X that a security incident had hit its systems. It asked RUM customers to remove its embed code from their websites. Production build data later showed the script was gone from the trading site.
RUM tools measure page speed and user experience, so many sites run them on every page. Monitoring tools can also run with wide access to a page, which is why security teams treat them as high-trust code. The exact attack method has not been published.
Supply-chain attacks work because a trusted script runs in every visitor’s browser, so one bad update can reach many users at once. Past incidents, such as the Keystone data breach that exposed customer shipping details, show how vendor weak spots can put crypto users at risk.
How Much Was Stolen: Latest Crypto Update on the Losses
Blockchain trackers such as Arkham and Bubblemaps estimated roughly $2.5 million to $2.7 million left about 700 to 710 wallets. The company has not confirmed these figures or shared an official total.
Item | Reported detail |
Estimated loss | $2.5M to $2.7M |
Wallets affected | About 700 to 710 |
Main token used | POL |
Attacker wallet peak | $2.65M to $2.7M |
Platform hit | International only |
Most funds were swapped into POL, the native token of Polygon, then moved to a suspected attacker wallet. That wallet peaked near $2.7 million before further transfers.
The gap between estimates and official data matters. Chain trackers can follow wallet flows, yet they cannot see the cause or confirm every victim. Treat the totals as estimates until the company shares its own count.
Polymarket Response: Trading Halt, Fix, and Reimbursement Plan
The company shared updates on its official X account and status page. Its main post said the issue was fixed and law enforcement had been notified. It added that “anyone who has been impacted will be made whole.”
About 2:05 p.m. ET: cancel-only mode, relayer actions paused
About 2:35 p.m. ET: fix announced, trading halted
About 3:05 p.m. ET: incident resolved, trading restored
On Discord, the company indicated that users who lost under $10,000 would see funds restored by October 30, 2026. Larger claims need a release form. Because DebugBear is UK-based, the case went to UK law enforcement. Follow our crypto security news for reimbursement updates.
Why This Second Vendor Incident Matters for Prediction Markets
This is the second recent third-party loss for the platform. A June 2026 front-end issue involved roughly $3 million, and the core contracts were unaffected.
The Polymarket security breach points to vendor risk, not smart contract risk. Users still lost money through a script on the website. Regulators are also watching every prediction market closely.
Security experts often advise cutting back on third-party scripts and checking vendor access on a regular basis. For users, the safest route for refund steps is the company’s official channels, not links sent by strangers.
Several details are still missing. The company has not said when claims above $10,000 will be paid, and no findings from UK law enforcement have been made public so far. It also has not confirmed a loss total or named the provider.
The Polymarket security breach started with an outside script, not the platform’s own contracts. Until more details come out, treat any refund message with care and check the latest crypto update first.
Disclaimer: This article is for educational and informational purposes only and should not be considered financial or investment advice. Always conduct your own research before making investment decisions.






