Zaif Email Leak Exposes 380,536 Addresses Could Phishing Hit Next?
Zaif Email Leak: 380,536 Addresses Exposed—What Users Must Know
Japanese crypto exchange Zaif has confirmed that a hacked service provider exposed 380,536 unique contact addresses.
In its second update of November 4, 2026, the company said the Zaif email leak involves addresses only, with no names, passwords, or trading records included.
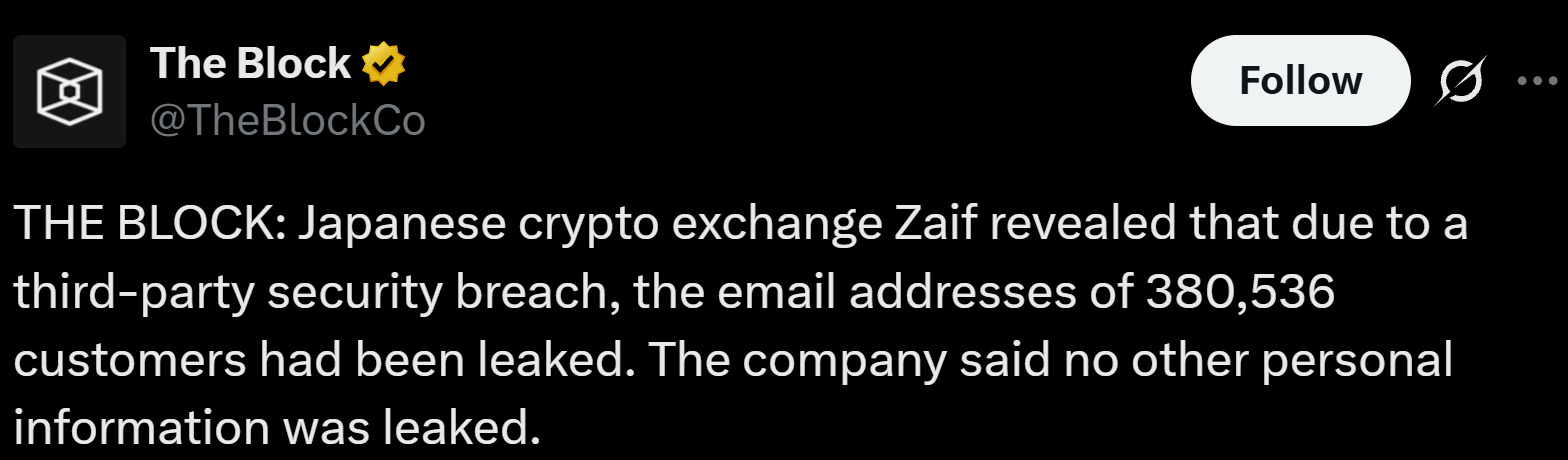
Source: The Block
What the Exchange Announced
The problem started at a vendor, not at the exchange. Arara Inc. runs “Arara Message,” the service the platform uses to send customer notices.
According to the first notice of November 2, a third party gained unauthorized access to the provider’s servers, and information flowed out, including from the environment Zaif used.
At that stage, nobody knew whether Zaif’s list was affected. The provider was still investigating, so Zaif issued an early warning.
The provider’s own disclosure is linked from both company notices for readers who want the provider’s side.
Timeline: From Warning to Confirmation
Events moved quickly across three days:
Date | What happened |
Nov 2, 2026 | The reports a server breach; Zaif posts an early warning. |
Nov 2, 2026 (night) | The confirms the registered contact entries were leaked. |
Nov 4, 2026 | Zaif receives the full list and publishes its second update. |
The count of 380,536 excludes duplicates, based on the provider’s report in the November 4 notice.
What Was and Was Not Exposed
The Zaif email leak is limited in scope, according to the company, but it still matters because those details can be misused.
Here is the breakdown:
Category | Status |
Contact entries | Leaked: 380,536 unique entries |
Names and other profile details | Not included |
Message contents | Not included |
Passwords and login credentials | Not stored with the provider, not leaked |
Home addresses, phone numbers | Not stored with the provider, not leaked |
Trading information | Not stored with the provider, not leaked |
Zaif’s own systems | No unauthorized access confirmed |
Two clarifications help avoid confusion. First, the figure counts unique entries, not confirmed active accounts.
The company says the list may include entries registered with in the past, and it is still working out how many belong to current customers.
Second, a leaked address alone cannot open an account, because the leaked data contains no login credentials.
So far, the exchange reports no secondary damage, such as unauthorized logins or asset outflows.
How to Protect Yourself From Phishing
The real risk after a Zaif email leak is fake messages. Criminals who hold such a list can send mail pretending to be the platform.
The company asks users to follow these rules if they receive anything suspicious:
Do not click links inside the message
Never open attachments
Do not type passwords or two-factor codes into any login page reached from a message
The company says it never asks customers for passwords or two-factor codes by mail.
It also suggests that customers who use mail-based verification consider switching to a more secure authenticator app for two-step login.
Because delivery of notices is paused, a message claiming to be from the exchange deserves extra suspicion right now.
Check the official website or the company’s verified social account instead. Questions can go through the support request form.
As general good practice, also be cautious of messages that create urgency, such as threats of account closure, or that come from sender names that look slightly different from the real one.
What the Company Says Happens Next
Delivery of regular notices is paused because the provider’s service has stopped. Updates will appear on the company’s website news page and official social account.
After sending resumes, affected customers will be contacted individually.
The notice lists further steps:
Reports have been made to the relevant authorities
The provider will be asked for a full explanation of the cause and prevention measures
The exchange will review what data it shares with vendors and how those suppliers protect it
Improvements will follow, including a possible change of suppliers
New facts will be published quickly if they emerge
The company also said it takes seriously the loss of customer information entrusted to a contractor.
The case shows a common weak point in digital services: outside suppliers. Even when a company’s own systems stay secure, data stored with a supplier can still escape.
That is why the planned review of supplier access and data-sharing scope is the most important item on the list.
Conclusion
The Zaif email leak is a supplier-side breach that exposed a large list of addresses but, per the exchange, nothing that grants account access.
The main danger is targeted phishing, so careful habits matter more than panic.
Watch the official channels for the next update, and consider moving to authenticator-based two-step login.
Anyone who gets an unexpected message about their account should pause, verify through official channels, and report it through the support form.
Disclaimer
This article is for educational and informational purposes only and is not financial or investment advice. Crypto assets are high risk, their prices can be very volatile, and you can lose some or all of your money. Always do your own research and consider speaking with a licensed financial advisor before making investment decisions.






