IOSCO Quantum Report Warns Crypto to Prepare Now
The IOSCO Quantum Report, a new 63-page study from the global body of securities regulators, warns that financial markets and the crypto industry should start getting ready now for the risks that quantum computers could bring to today’s security tools.
The report says no practical quantum computer can break widely used cryptography today, but it adds that moving blockchains to safer methods will take a long time, which is why crypto firms and wallet users are watching it closely.
Key Takeaways
The IOSCO Quantum Report was published on November 19, 2026, and runs 63 pages.
It says quantum computers able to break widely used cryptography do not exist yet, but preparation should begin now.
Conservative estimates put such machines in the 2030 to 2035 window, while some experts say to plan for five years.
Blockchains face a hard move because new signatures are much larger and upgrades need hard forks.
IOSCO says quantum will stay a priority in 2027.
What Is the IOSCO Quantum Report and Why Does It Matter for Crypto?
The International Organization of Securities Commissions, known as IOSCO, released its Final Report on the Implications of Quantum Computing on Financial Markets on November 19, 2026, using a survey of its members, talks with industry experts, and a review of existing research, as the IOSCO news release explains.
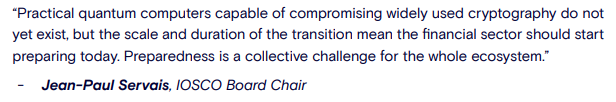
IOSCO board chair Jean-Paul Servais said the financial sector should “start preparing today,” and he described preparedness as a task for the whole ecosystem.
When Could Quantum Computers Break Crypto Security?
According to the full IOSCO report, conservative estimates place the arrival of quantum computers that can break today’s public-key cryptography between 2030 and 2035, although some industry participants say firms should plan for the chance that it happens within five years.
Public-key cryptography is the math that lets a wallet prove it owns its coins, so a machine able to break it would put those proofs at risk, but nothing like that exists today.
Why Post-Quantum Migration Is So Hard for Blockchains
Public blockchains such as Ethereum, Solana, and TRON rely on elliptic-curve cryptography that sits deep inside their core design, and the report says this makes the switch to post-quantum cryptography especially difficult.
One reason is size, since the new US standard called ML-DSA-44 uses signatures of about 2,420 bytes, which is 35 to 40 times larger than the common 64-byte signatures used now, and another reason is that the upgrades need hard forks, which are hard to push through on a decentralized network.
How Ready Is the Financial Sector for Quantum Risk?
IOSCO found that preparedness across the financial sector is still at an early stage and that real quantum uses in finance are also early and mostly experimental. The report is a call to act and not a new rule book, and IOSCO said it will keep quantum as a priority for 2027 with a focus on raising awareness across the financial ecosystem.
What Crypto Users and Firms Can Do Now
Nobody needs to move their coins today because of this report, but it is wise to follow the updates from the wallets, exchanges, and networks you use and to keep your software current.
Firms can start by listing where they use public-key cryptography, since that list shows which systems would need to change first, and readers should treat any claim of full quantum-proof protection with care until independent experts confirm it.
Disclaimer: This article is for information only and is not financial or investment advice. Crypto assets carry risk, including the loss of funds, so verify current details with official sources.






